
AI Act EU: Your Complete Guide to Compliance in 2026
The European Union's Artificial Intelligence Act represents the world's first comprehensive regulatory framework for artificial intelligence systems. As organisations across Europe adapt to these new requirements in 2026, understanding the ai act eu has become essential for businesses deploying AI technologies. This landmark legislation establishes a risk-based approach to AI governance, balancing innovation with fundamental rights protection. Whether you're a startup developing AI solutions or an enterprise implementing AI tools, the Act's provisions will shape how you design, deploy, and manage artificial intelligence systems.
Understanding the AI Act EU Framework
The ai act eu introduces a tiered regulatory system based on the risk level of AI applications. This approach ensures that high-risk systems face stringent requirements whilst allowing low-risk applications to operate with minimal constraints.
The Four Risk Categories
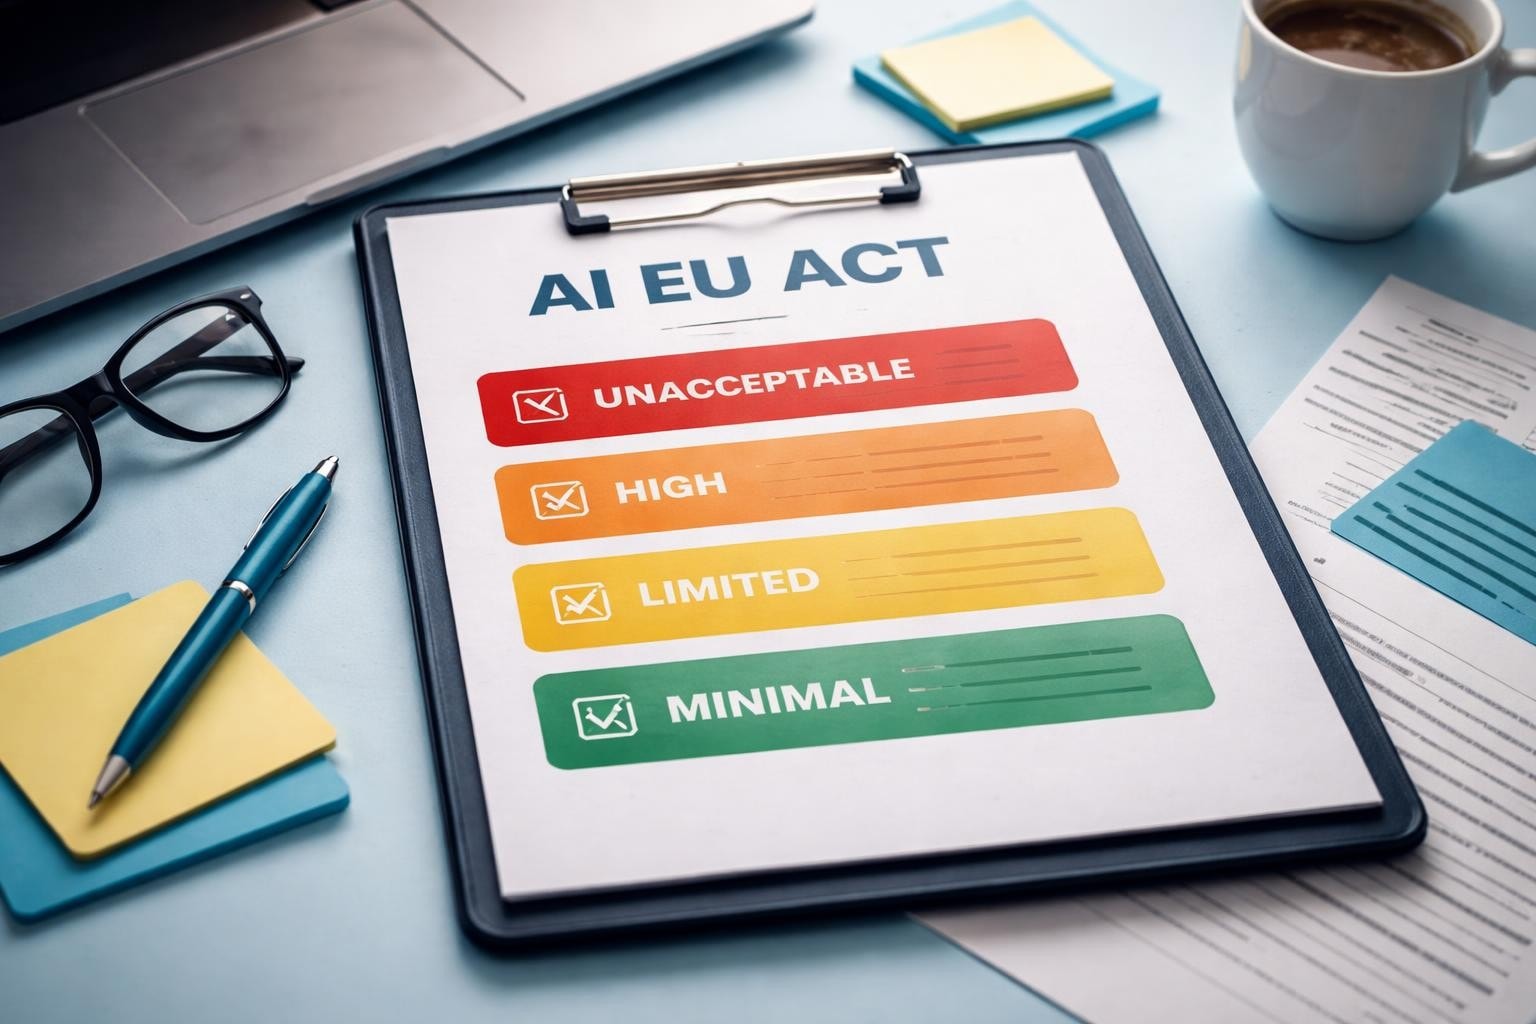
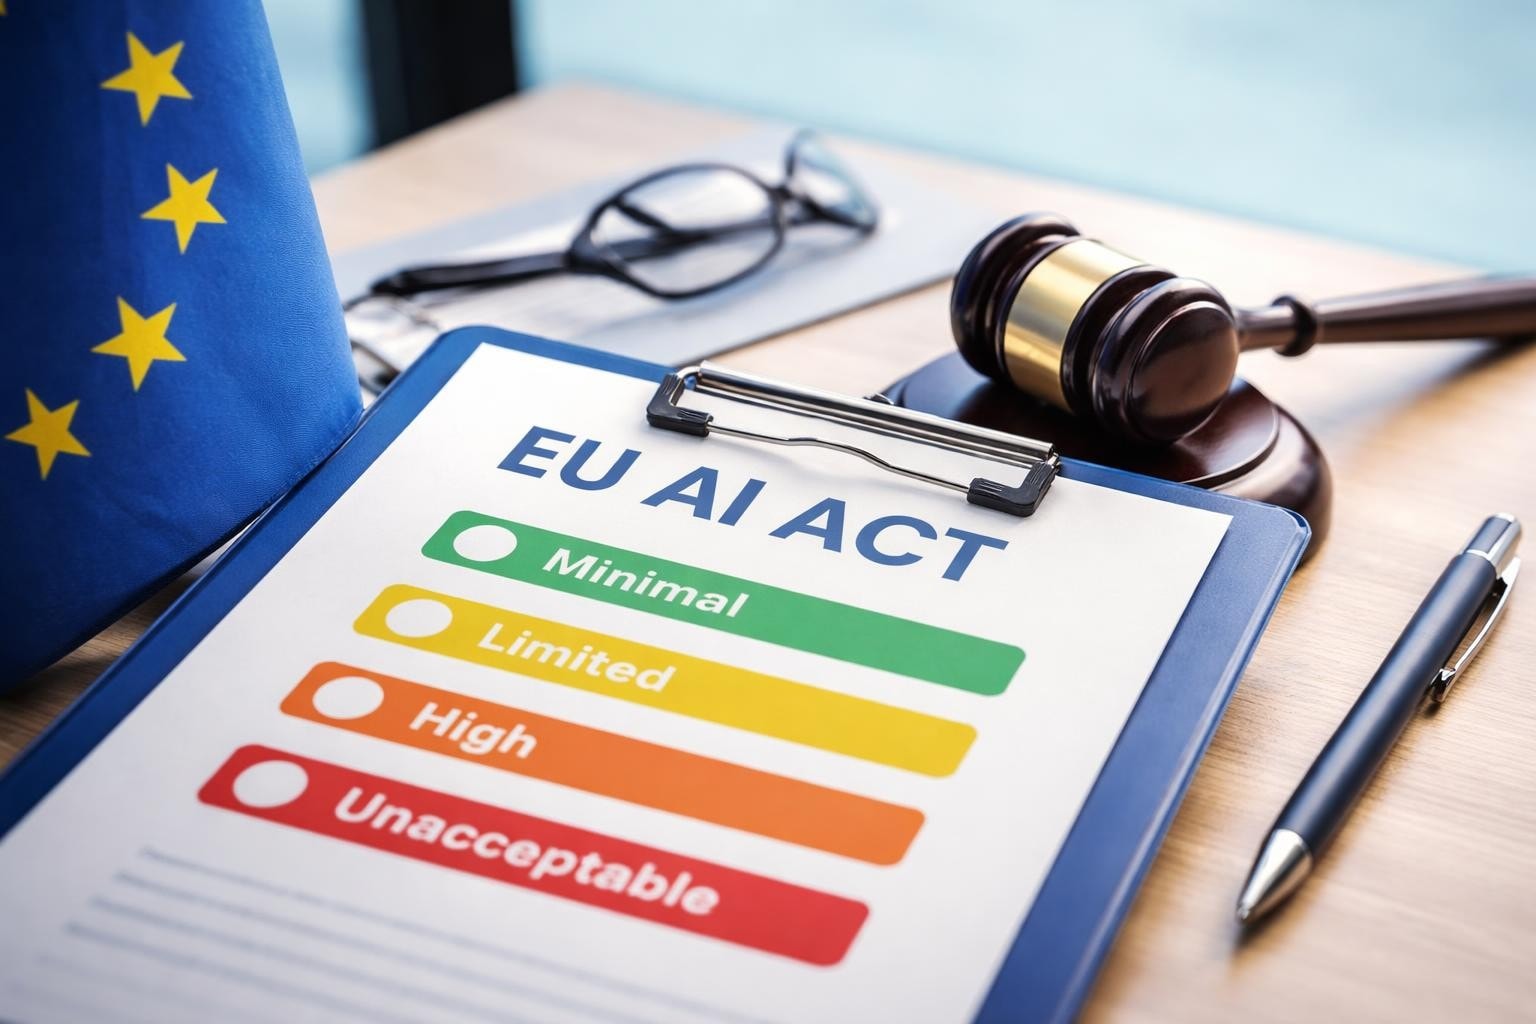
The legislation categorises AI systems into four distinct risk levels, each with corresponding obligations:
Risk Level | Examples | Requirements |
Unacceptable Risk | Social scoring, real-time biometric identification in public spaces | Prohibited entirely |
High Risk | AI in recruitment, credit scoring, law enforcement | Strict compliance, conformity assessments, transparency |
Limited Risk | Chatbots, AI-generated content | Transparency obligations, disclosure requirements |
Minimal Risk | AI-enabled video games, spam filters | No specific requirements beyond general law |
Understanding where your AI systems fall within this classification determines your compliance obligations. High-risk AI systems require comprehensive documentation, risk management systems, and human oversight mechanisms. Limited-risk applications primarily need clear disclosure that users are interacting with AI.
The European Data Protection Supervisor emphasises that these classifications aim to protect fundamental rights whilst fostering innovation. Systems that manipulate human behaviour or exploit vulnerabilities face outright bans, whilst others receive proportionate oversight.
Key Compliance Requirements Under the AI Act EU
Organisations deploying high-risk AI systems must implement robust governance frameworks. These requirements extend beyond technical specifications to encompass organisational processes and human oversight.
Essential Documentation and Transparency
High-risk AI providers must maintain technical documentation throughout the system's lifecycle. This includes:
Detailed descriptions of AI system capabilities and limitations
Training data characteristics and data governance measures
Risk management procedures and mitigation strategies
Human oversight mechanisms and their effectiveness
Conformity assessment documentation
Transparency requirements vary by risk level. For generative AI models, the ai act eu mandates disclosure of copyrighted training material and publication of detailed summaries about training content. The European Parliament notes these provisions aim to address concerns about intellectual property and content authenticity.
Data Governance and Quality Standards
AI systems perform only as well as their training data. The legislation requires:
Data relevance: Training datasets must be appropriate for the intended purpose
Data quality: Information must be accurate, complete, and representative
Bias mitigation: Providers must identify and address potential discrimination
Data documentation: Complete records of data sources, processing, and validation
These standards ensure AI systems don't perpetuate historical biases or produce unreliable outputs. Regular validation and testing throughout the AI lifecycle helps maintain compliance.
Implementation Timeline and Enforcement
The ai act eu follows a phased implementation schedule, with different provisions taking effect at various points. Understanding these deadlines helps organisations prioritise compliance activities.
Critical Compliance Dates
February 2025: Prohibition of unacceptable-risk AI systems entered force August 2026: General-purpose AI model obligations become applicable August 2027: Full compliance required for high-risk AI systems August 2030: Obligations extend to high-risk AI in certain legacy systems
This staggered approach gives organisations time to adapt existing systems and processes. However, businesses deploying new AI solutions must ensure immediate compliance with applicable provisions.
Enforcement mechanisms include substantial penalties for non-compliance. Violations can result in fines up to €35 million or 7% of global annual turnover, whichever is higher. The comprehensive FAQ from the European Commission provides detailed guidance on enforcement procedures and supervisory authorities.
Practical Steps for AI Act EU Compliance
Achieving compliance requires systematic planning and cross-functional collaboration. Organisations should begin with a comprehensive AI inventory and risk assessment.
Conducting an AI System Audit
Start by identifying all AI systems currently deployed or under development within your organisation. For each system, document:
Primary purpose and use cases
Data sources and processing methods
Deployment context and end users
Potential impact on individuals' rights
Current governance and oversight mechanisms
This inventory forms the foundation for risk classification. Many organisations discover they have more AI systems than initially recognised, including embedded AI in third-party software and automated decision-making tools.
Building a Compliance Framework
Once you've classified your AI systems, develop appropriate governance structures:
For high-risk systems:
Establish quality management systems aligned with ISO standards
Implement continuous monitoring and performance tracking
Create human oversight protocols with clear escalation procedures
Develop incident response and reporting mechanisms
For limited-risk systems:
Design clear AI disclosure mechanisms
Create user-friendly explanations of AI involvement
Document transparency measures and their effectiveness
For all systems:
Train relevant staff on ai act eu requirements
Integrate compliance into development workflows
Establish regular review and update procedures
AI Literacy as a Compliance Enabler
Effective compliance extends beyond legal and technical teams. The ai act eu explicitly requires AI literacy amongst those deploying and using AI systems. Article 4 mandates that providers and deployers ensure adequate AI literacy among staff.
Why AI Literacy Matters
Understanding AI fundamentals enables employees to:
Recognise when AI systems may produce biased or unreliable outputs
Implement effective human oversight and intervention
Communicate AI capabilities and limitations accurately
Identify potential compliance risks before they escalate
Make informed decisions about AI deployment and use
Organisations investing in comprehensive AI education demonstrate regulatory compliance whilst building a culture of responsible AI use. Training programmes should cover AI basics, ethical considerations, risk management, and specific regulatory requirements.
For businesses seeking structured compliance with Article 4 requirements, AI Literacy Course for EU AI Act Compliance offerings provide targeted training aligned with regulatory mandates, helping organisations meet their AI literacy obligations efficiently.
Navigating Industry-Specific Requirements
The ai act eu affects different sectors in distinct ways. Understanding sector-specific implications helps organisations focus their compliance efforts effectively.
High-Impact Sectors
Sector | Common High-Risk AI | Key Considerations |
Healthcare | Diagnostic systems, treatment recommendations | Patient safety, medical device regulations |
Finance | Credit scoring, fraud detection | Consumer protection, fair lending |
Human Resources | Recruitment screening, performance evaluation | Non-discrimination, employment law |
Law Enforcement | Predictive policing, biometric identification | Fundamental rights, data protection |
Healthcare providers deploying AI diagnostic tools must ensure systems meet both AI Act requirements and existing medical device regulations. Financial institutions need to demonstrate that AI-powered credit decisions comply with anti-discrimination laws whilst maintaining model explainability.
Recruitment AI presents particular challenges, as these systems frequently fall into the high-risk category. Employers must document how algorithms evaluate candidates, implement human review of AI recommendations, and regularly audit for discriminatory patterns.
Managing Third-Party AI Systems
Many organisations use AI systems developed by external providers. The ai act eu establishes clear responsibilities for both providers and deployers. As a deployer, you must:
Verify that providers have met their compliance obligations
Ensure AI systems are used according to intended purpose
Monitor system performance and report serious incidents
Maintain human oversight appropriate to the risk level
Provide deployer information to relevant authorities
Procurement processes should include AI Act compliance verification. Request documentation demonstrating conformity assessments, risk management procedures, and transparency measures from vendors.
The Global Impact of EU AI Regulation
Although enacted in Europe, the ai act eu influences AI governance worldwide. Its extraterritorial reach affects any organisation whose AI systems are used within the EU, regardless of where the provider is based.
International Compliance Considerations
Non-EU organisations must comply if they:
Place AI systems on the EU market
Provide AI outputs used within the EU
Deploy AI systems affecting people in the EU
This broad scope mirrors the GDPR's global impact. IBM's analysis suggests the Act will likely become a de facto global standard, as organisations find it easier to implement consistent AI governance across all markets rather than maintaining region-specific approaches.
The world's first comprehensive AI regulation status of the ai act eu positions it as a model for other jurisdictions developing AI laws. Understanding EU requirements provides valuable preparation for emerging regulations in other regions.
Voluntary Codes of Practice and Industry Response
Beyond mandatory requirements, the European Commission has released voluntary codes of practice to help businesses prepare for full implementation. These codes provide practical guidance on meeting AI Act obligations.
Industry Adoption Challenges
According to AP News reporting, whilst many major technology companies have signed onto these voluntary frameworks, some notable exceptions exist. Meta's refusal to participate, citing legal uncertainties about the AI code of practice, highlights ongoing debates about implementation details.
These voluntary initiatives cover:
Model transparency and documentation standards
Risk assessment methodologies
Testing and validation procedures
Incident reporting frameworks
Organisations participating in these programmes gain early insights into regulatory expectations and demonstrate proactive commitment to responsible AI. Even non-mandatory guidance helps clarify ambiguous requirements and establish industry best practices.
Building Long-Term AI Governance
Compliance with the ai act eu isn't a one-time project but an ongoing commitment. Successful organisations embed AI governance into their operational DNA through systematic processes and cultural change.
Establishing Governance Structures
Create dedicated oversight mechanisms appropriate to your organisation's size and AI deployment scale:
AI Governance Board: Senior leadership providing strategic direction and resource allocation AI Ethics Committee: Cross-functional team reviewing high-risk deployments and ethical considerations AI Compliance Team: Specialists managing documentation, assessments, and regulatory engagement AI Champions Network: Distributed advocates promoting responsible AI practices throughout the organisation
Regular governance reviews ensure frameworks remain effective as AI technologies and regulatory interpretations evolve. Quarterly assessments of AI systems, annual policy updates, and continuous staff education maintain compliance momentum.
Monitoring and Continuous Improvement
The ai act eu requires ongoing monitoring of AI system performance. Implement:
Automated performance tracking against defined metrics
Regular bias and fairness audits
User feedback mechanisms and complaint procedures
Incident logging and root cause analysis
Periodic third-party assessments
When monitoring reveals issues, respond promptly with corrective actions. Document all incidents, investigations, and remediation measures. This record demonstrates regulatory diligence and informs future improvements.
Preparing for Regulatory Evolution
AI regulation continues to develop as technologies advance and societal understanding deepens. The ai act eu includes provisions for regular review and updates, ensuring the framework remains relevant.
Staying Ahead of Changes
Monitor regulatory developments through:
Official European Commission publications and guidance
Industry association updates and working groups
Legal and compliance advisory services
Technology vendor communications about product updates
Academic research on AI governance and ethics
Participate in consultation processes when regulators seek stakeholder input. Your practical experience deploying AI systems provides valuable perspective that shapes implementation guidance and future amendments.
Building flexibility into your compliance framework allows rapid adaptation to regulatory changes. Modular governance processes, well-documented systems, and cross-trained staff enable swift responses to new requirements.
The ai act eu fundamentally reshapes how organisations develop, deploy, and manage artificial intelligence systems across Europe and beyond. By understanding risk classifications, implementing robust governance frameworks, and investing in AI literacy, businesses can achieve compliance whilst maintaining innovation momentum. GURO (myaitraining.eu) provides AI Literacy courses fully aligned with Article 4 of the EU AI Act, delivering essential AI understanding through interactive, self-paced training available in over 30 languages. Start building your organisation's AI compliance foundation today with structured learning that meets regulatory requirements whilst empowering your workforce.
Comments