
AI Act European Commission: Your 2026 Compliance Guide
The ai act european commission framework represents one of the most significant regulatory developments in technology governance worldwide. As we navigate through 2026, organisations across the European Union face increasing pressure to align their artificial intelligence systems with comprehensive legal requirements. The regulation, which entered into force in August 2024, is now actively shaping how businesses deploy, develop, and manage AI technologies. Understanding the nuances of this legislation is no longer optional for companies operating within the EU market.
Understanding the AI Act European Commission Framework
The European Commission's regulatory framework for AI establishes a risk-based approach to artificial intelligence governance. This methodology categorises AI systems according to their potential impact on fundamental rights and safety, creating distinct compliance pathways for different use cases.
Risk Classification System
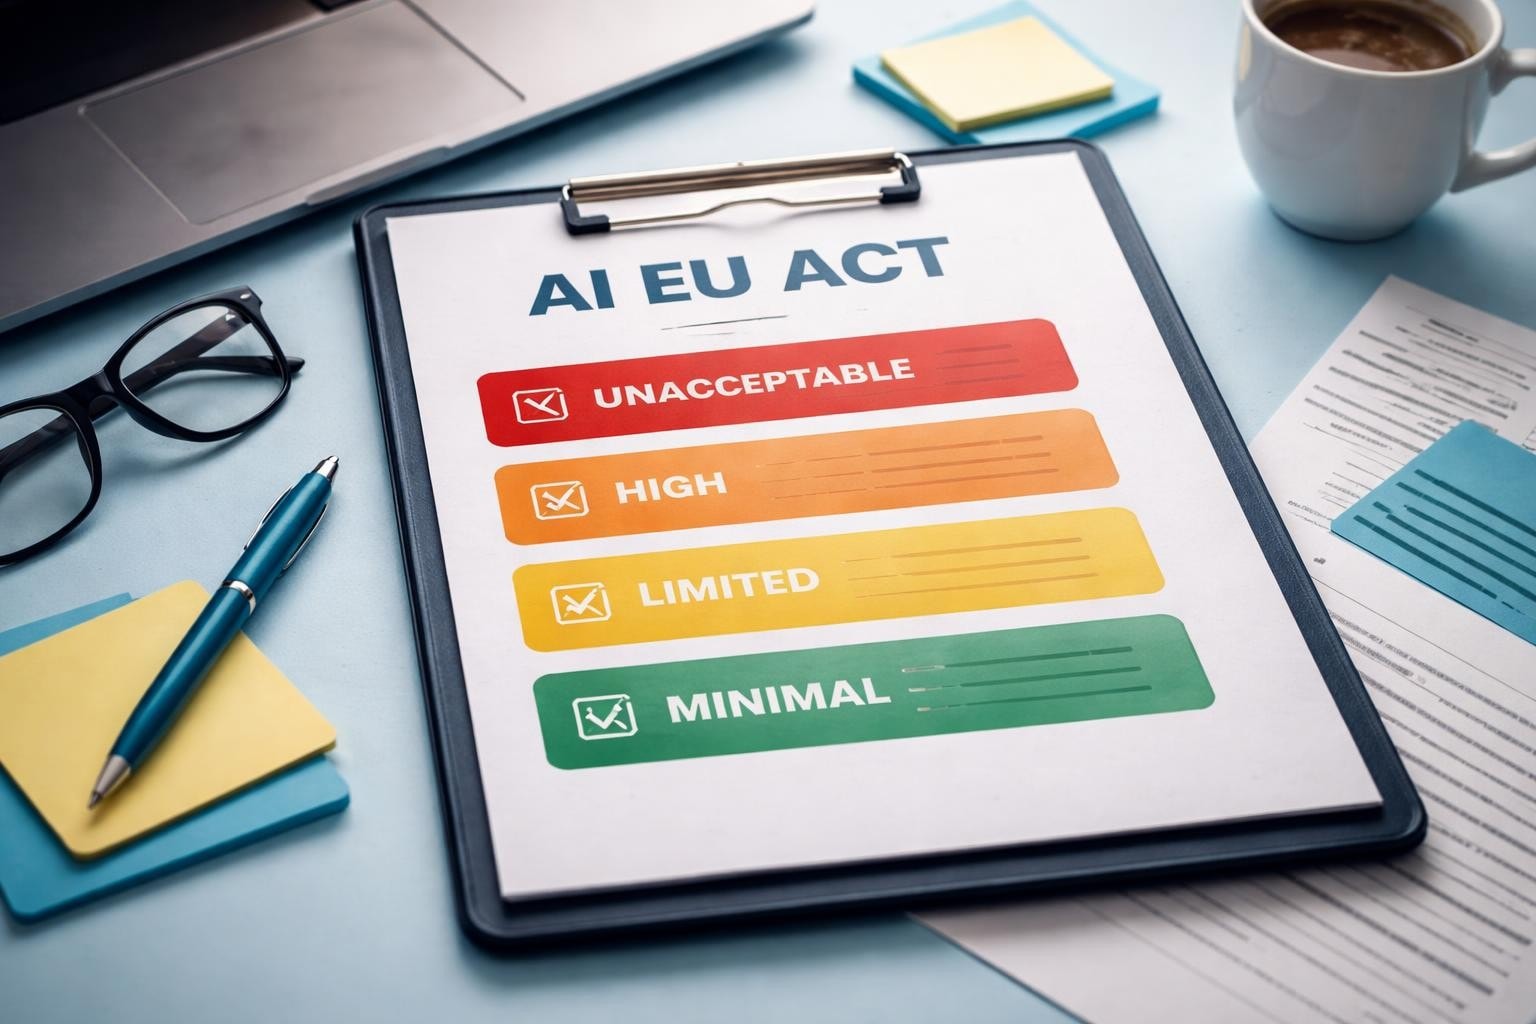
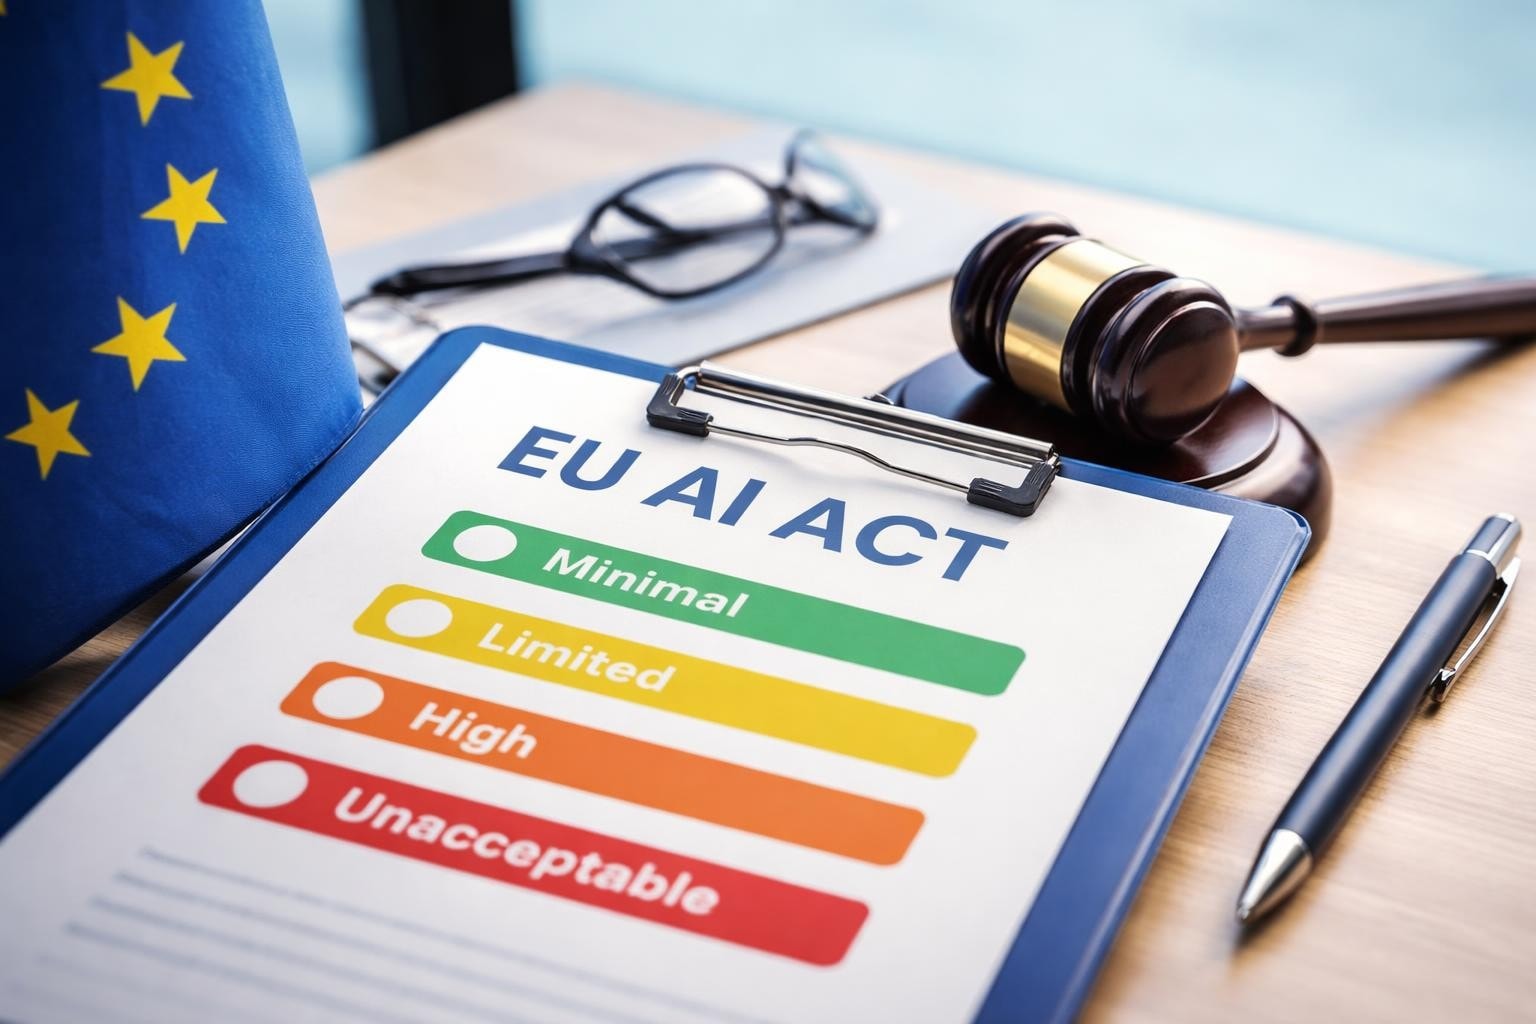
The ai act european commission structure divides AI systems into four primary risk categories, each carrying different obligations:
Unacceptable risk: Banned AI practices that violate fundamental rights
High-risk: Systems requiring strict compliance measures and conformity assessments
Limited risk: Applications with specific transparency obligations
Minimal risk: Systems with voluntary codes of conduct
This tiered approach allows organisations to focus resources where regulatory scrutiny is most intense. High-risk AI systems, for instance, must meet stringent requirements around data governance, technical documentation, and human oversight.
Key Provisions and Requirements
When the AI Act officially entered into force, it triggered a phased implementation timeline. Organisations must now prepare for multiple compliance deadlines that extend through 2027 and beyond.
The regulation mandates several fundamental requirements for high-risk AI systems:
Risk management systems that identify and mitigate potential harms throughout the AI lifecycle
Data governance measures ensuring training datasets are relevant, representative, and free from bias
Technical documentation providing comprehensive information about system design and capabilities
Transparency obligations enabling users to understand when they interact with AI systems
Human oversight mechanisms allowing intervention in automated decision-making processes
Implementation Timeline and Compliance Deadlines
The ai act european commission enforcement schedule follows a carefully structured rollout. Understanding these dates is crucial for strategic planning.
Compliance Milestone | Effective Date | Scope |
Prohibited AI Practices | February 2025 | Ban on unacceptable risk systems |
General Purpose AI Rules | August 2025 | Transparency for GPAI models |
High-Risk System Requirements | August 2026 | Full conformity assessments |
Extended Transition Period | August 2027 | Legacy systems compliance |
By August 2026, high-risk AI systems must achieve full conformity with all applicable requirements. This deadline is particularly significant as it represents the point at which enforcement activities intensify across member states.
Phased Approach Benefits
The graduated timeline allows organisations to prioritise compliance activities. Companies can begin with prohibited practices, ensuring no AI systems violate fundamental rights. Subsequently, they can address transparency requirements before tackling the comprehensive conformity assessments required for high-risk applications.
Governance and Enforcement Mechanisms
The governance structure established under the AI Act creates a multi-layered enforcement ecosystem. At the European level, the newly established AI Office coordinates implementation activities and provides guidance to member states.
Institutional Responsibilities
National competent authorities in each member state bear primary responsibility for enforcement within their jurisdictions. These bodies conduct market surveillance, investigate complaints, and impose penalties for non-compliance. The European AI Board provides coordination and consistency across borders, ensuring harmonised interpretation of the regulation.
Market surveillance authorities possess significant powers:
Requesting documentation and information from AI system providers
Conducting inspections of premises and technical systems
Ordering withdrawal or recall of non-compliant AI systems
Imposing administrative fines for violations
Penalty Structure
Financial penalties under the ai act european commission regime can reach substantial amounts. The regulation establishes proportionate fines based on violation severity:
Violation Type | Maximum Fine |
Prohibited AI practices | €35 million or 7% of global turnover |
Non-compliance with AI system requirements | €15 million or 3% of global turnover |
Incorrect or incomplete information | €7.5 million or 1% of global turnover |
These penalties apply to whichever amount is higher, ensuring meaningful consequences for both large corporations and smaller enterprises. The enforcement measures create strong incentives for proactive compliance.
Standardisation and Technical Compliance
The standardisation programme under the AI Act plays a crucial role in operationalising legal requirements. Harmonised European standards provide presumption of conformity, offering organisations a clear pathway to demonstrate compliance.
Role of Harmonised Standards
When businesses implement systems according to approved harmonised standards, they benefit from presumption of conformity with corresponding legal requirements. This mechanism reduces uncertainty and provides practical guidance for technical implementation.
The European Commission has issued standardisation requests to CEN-CENELEC, the European standardisation organisations, covering areas such as:
Risk management methodologies for AI systems
Data quality and governance frameworks
Transparency and information provision requirements
Human oversight architectures
Robustness and accuracy metrics
Training Requirements Under Article 4
Article 4 of the ai act european commission framework establishes explicit obligations around AI literacy for personnel involved with high-risk AI systems. This provision recognises that technical compliance alone is insufficient without competent human oversight.
Organisations deploying high-risk AI systems must ensure staff possess appropriate levels of AI literacy, including understanding of:
The AI system's capabilities and limitations
Appropriate interpretation of output
Potential risks and mitigation strategies
Human oversight responsibilities
Fundamental rights considerations
Building AI Literacy Programmes
Effective AI literacy training programmes address both technical and ethical dimensions. Personnel must grasp how AI systems function whilst appreciating broader implications for fairness, transparency, and accountability. Organisations operating across multiple European markets face additional complexity, as training materials must often be delivered in various languages to accommodate diverse workforces.
For companies seeking to meet Article 4 requirements efficiently, structured training solutions can significantly accelerate compliance. The AI Literacy Course for EU AI Act Compliance provides enterprises with scalable training options, offering interactive content in over 30 languages designed specifically around regulatory requirements. This approach ensures consistent quality across different locations whilst allowing employees to learn at their own pace.
Sector-Specific Implications
The ai act european commission regulation affects different industries with varying intensity. Sectors already subject to strict regulation, such as healthcare and financial services, face layered compliance obligations.
High-Risk Sectors
Certain domains automatically classify as high-risk under the AI Act due to their potential impact on safety and fundamental rights:
Healthcare: AI for diagnosis, treatment planning, and patient monitoring
Critical infrastructure: Systems managing energy grids, water supply, and transport
Education: AI determining educational pathways or examination scores
Employment: Recruitment tools, performance evaluation systems, and workforce management
Law enforcement: Biometric identification and predictive policing applications
Each sector must navigate specific technical requirements whilst maintaining compliance with existing domain regulations. For instance, healthcare AI systems must satisfy both the AI Act and medical device regulations.
Small and Medium Enterprises
The regulation includes proportionality considerations for SMEs, recognising resource constraints. Whilst legal obligations remain consistent, the European Commission's strategy emphasises support mechanisms including regulatory sandboxes and guidance documents tailored to smaller organisations.
SMEs benefit from priority access to AI regulatory sandboxes, controlled environments where innovative AI systems can be tested under regulatory supervision. These facilities reduce compliance costs whilst accelerating time to market.
International Dimensions and Global Impact
The ai act european commission approach is influencing regulatory developments worldwide. Similar to how GDPR became a global privacy benchmark, the AI Act is shaping international discussions about AI governance.
Extraterritorial Application
The regulation applies to AI systems placed on the EU market or affecting EU persons, regardless of provider location. This extraterritorial reach means organisations outside Europe must comply when their AI systems serve European users.
Third-country providers face equivalent obligations to European companies, including:
Appointing authorised representatives within the EU
Ensuring AI systems meet all applicable requirements
Providing technical documentation to market surveillance authorities
Implementing post-market monitoring systems
Global Regulatory Convergence
Several jurisdictions are developing AI regulations inspired by the European model. This convergence creates opportunities for organisations implementing robust compliance programmes, as investments in meeting EU requirements often facilitate compliance elsewhere. Understanding the full legislative text provides valuable insights for global AI governance strategies.
Building Organisational Readiness
Achieving ai act european commission compliance requires coordinated efforts across multiple organisational functions. Legal, technical, and operational teams must collaborate on implementation strategies.
Essential Preparation Steps
Organisations should prioritise these foundational activities:
Inventory and classification: Identify all AI systems within the organisation and classify them according to risk categories. This mapping exercise reveals which systems require immediate attention.
Gap analysis: Compare current practices against AI Act requirements, identifying areas requiring enhancement. Document findings systematically to support implementation planning.
Governance structures: Establish clear accountability for AI compliance, including designated roles, reporting lines, and decision-making processes.
Documentation frameworks: Develop templates and procedures for technical documentation, risk assessments, and conformity declarations required under the regulation.
Vendor management: Review supplier relationships for AI components and services, ensuring contractual arrangements address compliance responsibilities.
Internal Capabilities Development
Beyond formal compliance activities, organisations benefit from cultivating internal AI expertise. The European Commission's own AI implementation strategy demonstrates how public sector entities are approaching these challenges, offering lessons for private organisations.
Building AI literacy throughout the organisation creates competitive advantages beyond regulatory compliance. Employees who understand AI capabilities and limitations make better decisions about technology adoption, usage, and oversight. Comprehensive training programmes should reach beyond technical teams to encompass managers, executives, and frontline personnel interacting with AI systems. Resources available through platforms like GURO enable organisations to deploy consistent training across multiple locations and languages.
Monitoring and Continuous Compliance
The ai act european commission framework establishes ongoing obligations that extend beyond initial conformity assessments. Organisations must maintain compliance throughout AI system lifecycles.
Post-Market Monitoring Requirements
Providers of high-risk AI systems must implement post-market monitoring systems that actively collect and analyse data about system performance. This surveillance enables early detection of issues and informs necessary corrective actions.
Key monitoring activities include:
Collecting user feedback and incident reports
Analysing system performance against initial specifications
Identifying emerging risks or unexpected behaviours
Implementing corrective measures when issues arise
Maintaining comprehensive records of monitoring activities
Incident Reporting Obligations
Serious incidents involving high-risk AI systems trigger mandatory reporting to market surveillance authorities. These notifications must occur promptly, enabling regulatory oversight and preventing wider harms. The comprehensive overview of the AI Act details these procedural requirements alongside broader regulatory context.
Strategic Opportunities Within Compliance
Whilst compliance requirements impose obligations, they simultaneously create competitive advantages for organisations that embrace them strategically. Robust AI governance frameworks build customer trust, enhance brand reputation, and open access to risk-conscious market segments.
Competitive Differentiation
Demonstrating compliance through third-party certification or transparent documentation differentiates organisations in competitive markets. Business customers increasingly prioritise suppliers with verified AI governance practices, particularly in regulated sectors.
Organisations can leverage compliance investments by:
Publicising conformity certifications and assessments
Integrating AI governance into corporate sustainability reporting
Participating in industry initiatives and standard-setting processes
Contributing thought leadership on responsible AI practices
Innovation Within Boundaries
The ai act european commission framework establishes clear boundaries within which innovation can flourish. Rather than constraining development, these guardrails provide certainty about acceptable practices. Organisations investing in compliant AI development position themselves for sustainable growth as regulatory scrutiny intensifies globally.
The AI Act represents a transformative shift in how organisations must approach artificial intelligence, establishing comprehensive requirements that extend from system design through operational deployment. As enforcement activities intensify through 2026 and beyond, proactive compliance becomes essential for maintaining market access and avoiding substantial penalties. Meeting Article 4's AI literacy requirements ensures your workforce possesses the knowledge needed for effective human oversight whilst building broader organisational capabilities. GURO (myaitraining.eu) delivers AI literacy training specifically aligned with EU AI Act requirements, offering interactive courses in over 30 languages to support your compliance journey efficiently and effectively.
Comments