
AI EU: Navigating Compliance and Literacy in 2026
The intersection of artificial intelligence and European Union regulation represents one of the most significant business transformation challenges of this decade. As organisations across Europe implement AI systems, understanding the regulatory framework has become essential for operational success. The ai eu landscape encompasses comprehensive legislation, enforcement mechanisms, and practical compliance requirements that affect businesses of all sizes. With the AI Act entering various stages of implementation throughout 2026, organisations must navigate complex requirements whilst maintaining competitive advantage through intelligent technology adoption.
Understanding the AI EU Regulatory Framework
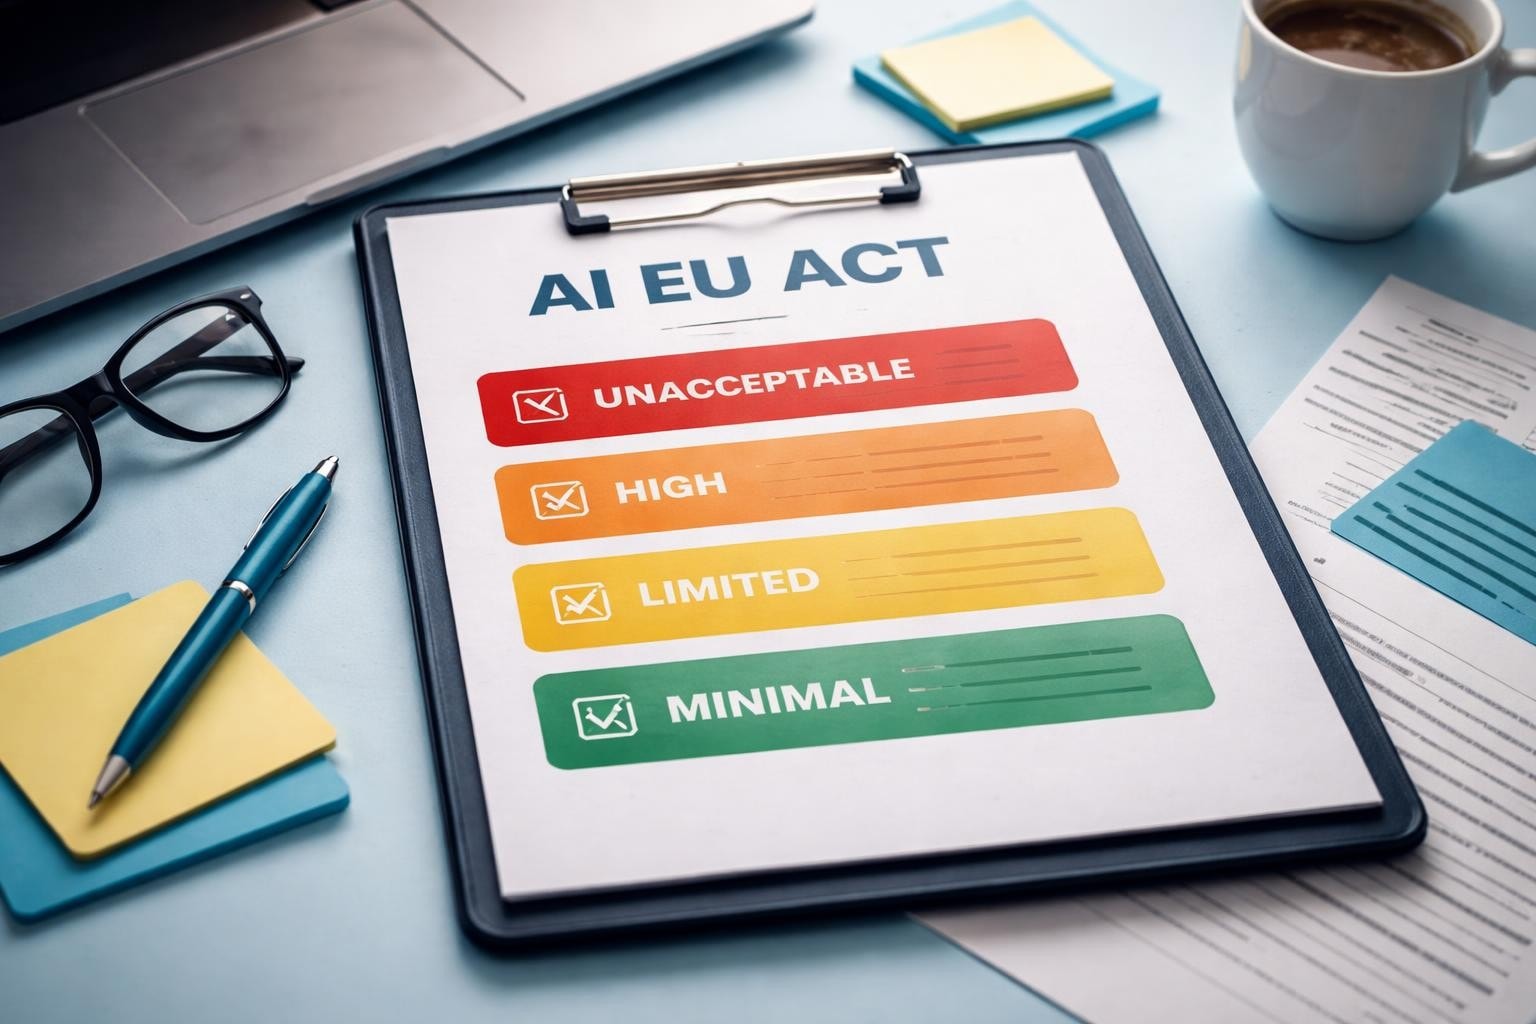
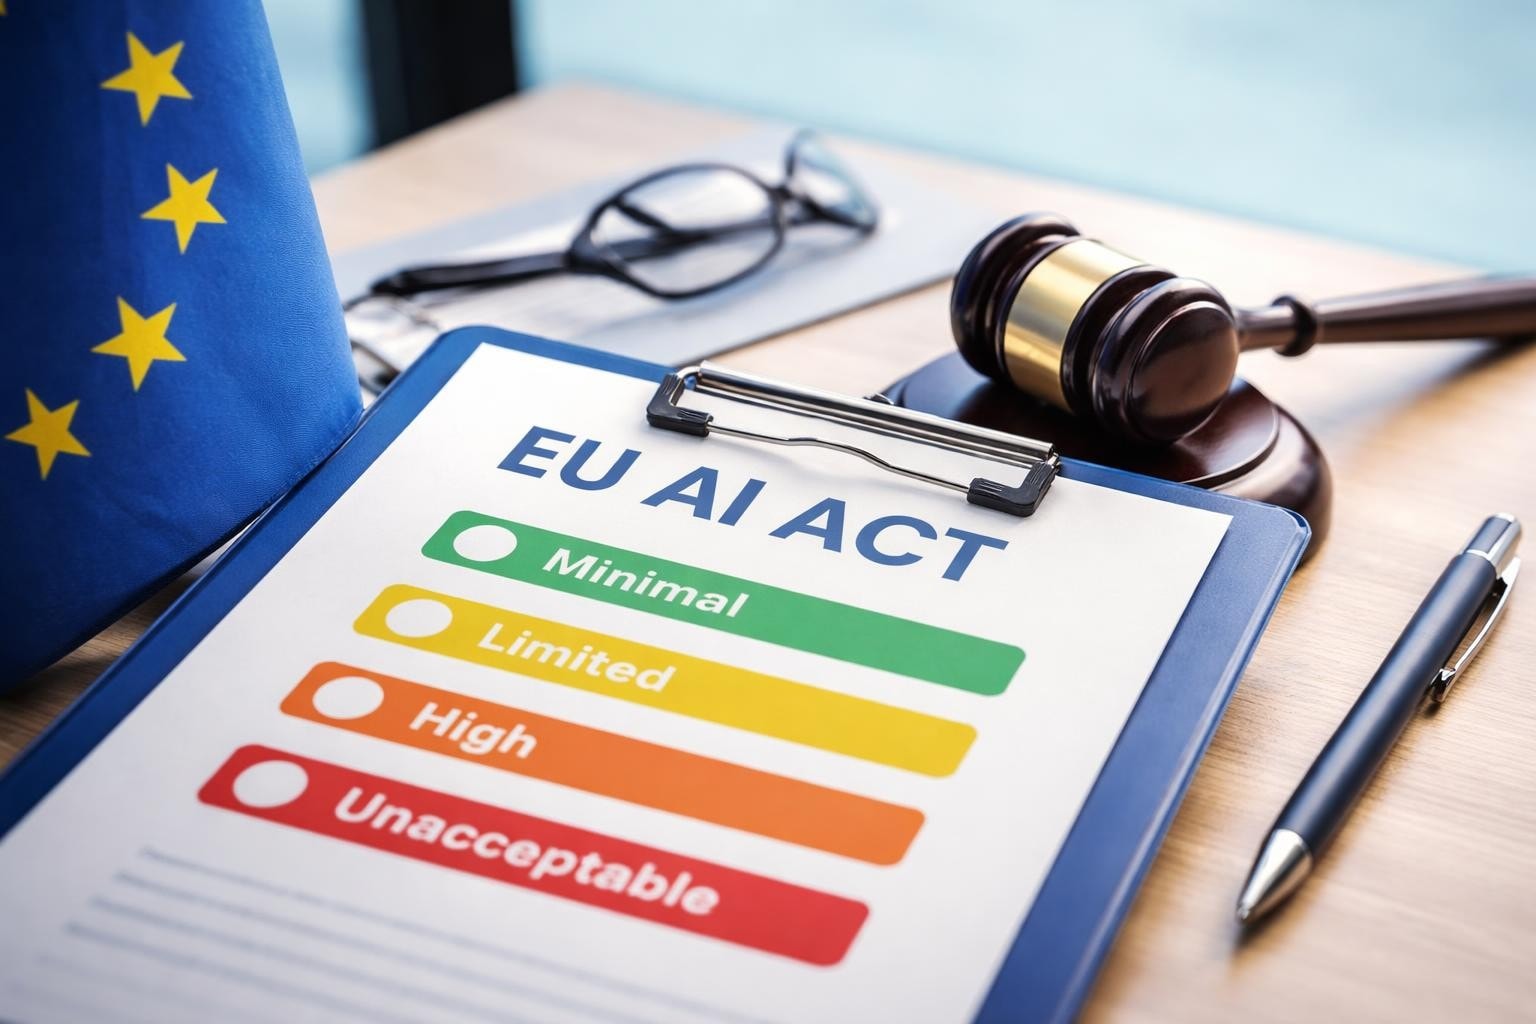
The European Union's approach to AI regulation establishes a risk-based framework that categorises artificial intelligence systems according to their potential impact on fundamental rights and safety. This comprehensive legislation, formally known as the AI Act, creates four distinct risk categories: unacceptable risk, high risk, limited risk, and minimal risk.
Unacceptable risk systems face outright prohibition within EU territories. These include AI applications that deploy subliminal manipulation, exploit vulnerabilities of specific groups, enable social scoring by public authorities, or facilitate real-time biometric identification in public spaces for law enforcement purposes (with narrow exceptions).
High-risk AI systems require rigorous compliance measures before deployment. These applications span eight specific domains:
Biometric identification and categorisation of natural persons
Management and operation of critical infrastructure
Educational and vocational training access
Employment, workers management, and self-employment access
Essential private and public services access
Law enforcement applications
Migration, asylum, and border control management
Administration of justice and democratic processes
Compliance Obligations for High-Risk Systems
Organisations deploying high-risk AI systems must establish comprehensive quality management systems, maintain detailed technical documentation, implement automatic logging capabilities, and ensure human oversight mechanisms. The transparency requirements extend to providing clear information about the AI system's capabilities, limitations, and intended purpose.
Risk management processes must operate throughout the AI system's lifecycle, from design through deployment and monitoring. Data governance protocols ensure training datasets meet quality standards, relevance requirements, and representativeness criteria to minimise bias and discrimination risks.
The Business Impact of AI EU Legislation
The ai eu regulatory environment creates both challenges and opportunities for organisations operating within European markets. Compliance costs vary significantly based on system risk classification, with high-risk applications requiring substantial investment in documentation, testing, and ongoing monitoring infrastructure.
Risk Level | Key Requirements | Typical Compliance Cost | Timeline |
Unacceptable | Complete prohibition | N/A (cannot deploy) | Immediate |
High | Full conformity assessment | €50,000-€500,000+ | 24-36 months |
Limited | Transparency obligations | €5,000-€25,000 | 6-12 months |
Minimal | Self-regulation | Minimal | Ongoing |
Small and medium enterprises face particular challenges adapting to these requirements. The European Commission recognises this burden and provides regulatory sandboxes, simplified compliance procedures for certain categories, and technical support through initiatives like AI Watch.
Strategic Advantages Through Early Compliance
Forward-thinking organisations treat ai eu compliance as competitive differentiation rather than regulatory burden. Early adoption demonstrates commitment to ethical AI practices, builds customer trust, and positions companies favourably for public sector contracts that increasingly prioritise compliant AI solutions.
The regulatory clarity provided by the AI Act reduces uncertainty in long-term technology planning. Organisations can invest confidently in AI systems knowing the compliance framework remains stable and predictable.
AI Literacy Requirements Under Article 4
Article 4 of the EU AI Act mandates that providers and deployers ensure personnel operating high-risk AI systems possess adequate AI literacy. This requirement recognises that technical compliance alone cannot guarantee responsible AI deployment without knowledgeable human oversight.
AI literacy encompasses understanding AI systems' capabilities and limitations, recognising potential risks and biases, interpreting AI outputs correctly, and knowing when human intervention becomes necessary. The legislation requires organisations to demonstrate that staff members interacting with high-risk systems receive appropriate training.
Training programmes must address:
Fundamental AI concepts and terminology
Specific system functionality and limitations
Risk identification and mitigation strategies
Data quality and bias recognition
Human oversight responsibilities
Incident reporting procedures
For organisations seeking structured compliance with these requirements, the AI Literacy Course for EU AI Act Compliance provides comprehensive training aligned specifically with Article 4 mandates, available across multiple enterprise tiers to accommodate organisations from 20 to over 250 employees.
Implementation Strategies for AI EU Compliance
Successful ai eu compliance requires systematic planning and phased implementation. Organisations should begin with comprehensive AI system inventory, categorising existing and planned applications according to risk classification frameworks established in the legislation.
Phase One: Assessment and Classification
Initial assessment identifies which AI systems fall within regulatory scope. Many organisations discover their AI footprint exceeds initial estimates once they account for embedded AI in third-party software, automated decision systems, and predictive analytics tools.
Classification determines applicable requirements for each system. This process requires technical expertise combined with legal interpretation, as borderline cases may demand careful analysis.
Phase Two: Gap Analysis and Planning
Gap analysis compares current practices against regulatory requirements, identifying specific deficiencies in documentation, risk management, data governance, or human oversight. Priority ranking helps organisations address highest-risk gaps first whilst developing longer-term compliance roadmaps.
Resource allocation must account for both initial compliance costs and ongoing maintenance requirements. The European Data Protection Supervisor provides guidance on integrating AI Act compliance with existing GDPR obligations.
Phase Three: Implementation and Documentation
Implementation executes planned compliance measures, establishing quality management systems, creating required documentation, and implementing technical controls. Documentation standards require precision and completeness, as regulatory authorities may request evidence during audits or investigations.
Training deployment ensures all relevant personnel understand their responsibilities under the ai eu framework. Different roles require tailored training content, from executive oversight to technical operation and compliance management.
The European AI Ecosystem Beyond Regulation
The ai eu landscape extends beyond regulatory compliance to encompass significant investment in AI research, infrastructure, and industrial capacity. The European AI in Science Strategy demonstrates the bloc's commitment to advancing AI capabilities whilst maintaining ethical frameworks.
Recent infrastructure initiatives include substantial investment in AI-optimised data centres. The EU's planned €30 billion investment in gigawatt AI data centres signals recognition that regulatory leadership must pair with computational capacity to maintain European competitiveness in AI development.
Hardware sovereignty receives attention through initiatives like the NanoIC semiconductor pilot facility, addressing supply chain vulnerabilities whilst developing next-generation chips optimised for AI workloads.
Voluntary Compliance and Industry Standards
Whilst mandatory requirements apply to high-risk systems, the European Commission encourages voluntary compliance frameworks for lower-risk applications. The voluntary code of practice for general-purpose AI released in 2026 helps businesses align with regulatory expectations even before formal obligations apply.
Industry-specific standards continue evolving to address sector-particular ai eu challenges. Financial services, healthcare, and manufacturing sectors develop tailored compliance frameworks that integrate AI Act requirements with existing regulatory obligations.
Professional certification programmes emerge as organisations seek standardised methods for demonstrating AI literacy and compliance expertise. These credentials help individuals advance careers whilst providing organisations with verifiable evidence of workforce capability.
Cross-Border AI Operations and Enforcement
Organisations operating across multiple jurisdictions face complexity when ai eu requirements intersect with other regulatory frameworks. The AI Act's extraterritorial application means non-EU organisations must comply when placing AI systems on the European market or when system outputs affect EU residents.
Enforcement mechanisms include market surveillance authorities in each member state, coordinated through a European Artificial Intelligence Board. Penalties for non-compliance reach up to €35 million or 7% of global annual turnover, whichever proves higher, for the most serious violations.
Harmonisation efforts aim to ensure consistent interpretation and application across member states, though implementation variations inevitably emerge. Organisations benefit from monitoring guidance issued by authorities in their primary operating jurisdictions whilst maintaining awareness of broader EU-level interpretations.
Practical Steps for Immediate Action
Organisations beginning their ai eu compliance journey should prioritise several immediate actions regardless of current maturity level. Establishing executive sponsorship ensures adequate resources and organisational priority for compliance initiatives.
Creating cross-functional compliance teams brings together legal, technical, operational, and risk management expertise. No single function possesses complete knowledge required for effective AI Act compliance.
Documentation practices should begin immediately, even for systems not yet classified as high-risk. Comprehensive records of AI system development, deployment decisions, and operational performance create valuable evidence whilst supporting ongoing risk assessment.
Exploring resources available through myaitraining.eu provides accessible pathways to building organisational AI literacy, with courses available in over 30 languages to accommodate diverse European workforces.
Looking Forward: The Evolution of AI EU Policy
The ai eu landscape will continue evolving as technology advances and practical implementation experience accumulates. The AI Act includes review mechanisms and adaptation procedures allowing regulatory frameworks to respond to emerging challenges without requiring complete legislative revision.
Stakeholder engagement remains crucial as authorities develop implementing acts, technical standards, and interpretive guidance. Organisations participating in consultation processes influence practical compliance requirements whilst gaining early insight into regulatory direction.
International AI governance discussions increasingly reference the EU approach as potential global standard. Organisations building robust ai eu compliance capabilities position themselves advantageously for expanding international AI governance requirements.
The balance between innovation and regulation continues generating debate, with some arguing current requirements impose excessive burden whilst others advocate for strengthened protections. Monitoring these discussions helps organisations anticipate potential regulatory evolution.
Successfully navigating the ai eu landscape requires combining regulatory compliance with genuine commitment to responsible AI development and deployment. Building organisational AI literacy represents the foundation for both meeting legal obligations and realising AI technology's full potential whilst managing associated risks. GURO (myaitraining.eu) delivers Article 4-aligned AI literacy training in a practical, self-paced format designed to help organisations across Europe meet compliance requirements whilst empowering their workforce with essential AI understanding. Start building your compliance-ready, AI-literate organisation today.
Comments