
EU Act AI: Compliance Guide for 2026 and Beyond
The European Union's Artificial Intelligence Act represents the world's first comprehensive legal framework governing artificial intelligence systems. As of 2026, organisations across Europe and beyond face mounting pressure to understand and comply with this landmark regulation. The eu act ai establishes a risk-based approach to AI governance, creating clear categories of prohibited practices, high-risk systems, and lower-risk applications. Whether you're deploying AI in healthcare, finance, human resources, or customer service, understanding the eu act ai requirements is no longer optional. It's a fundamental business necessity that demands immediate attention and strategic planning.
Understanding the EU AI Act Framework
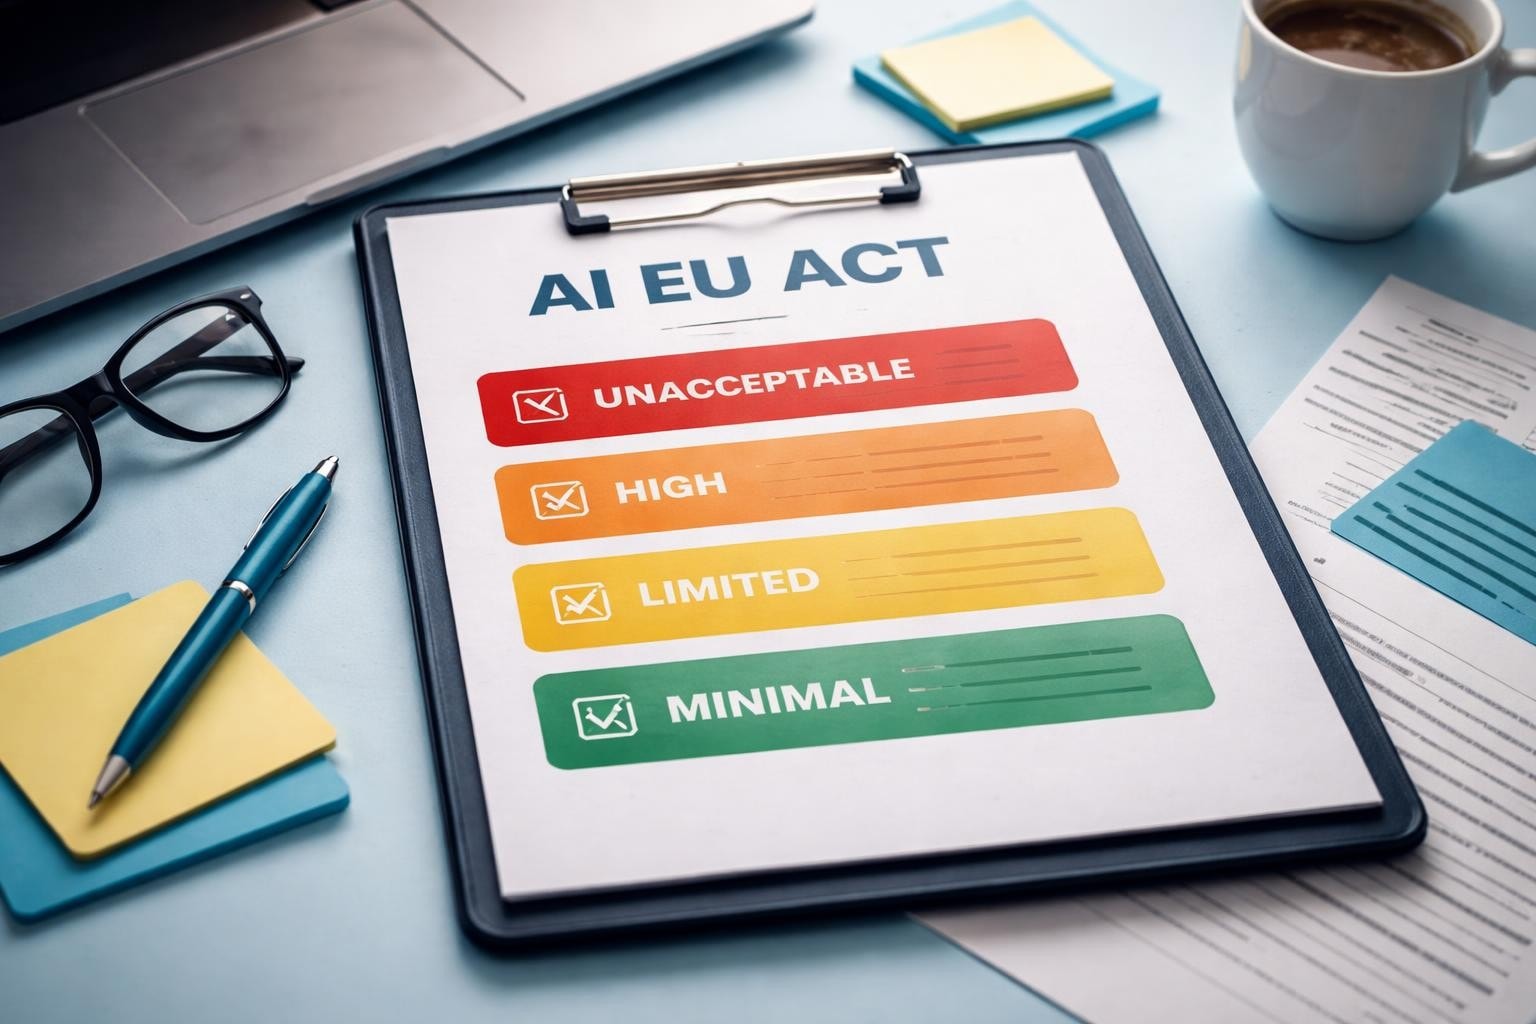
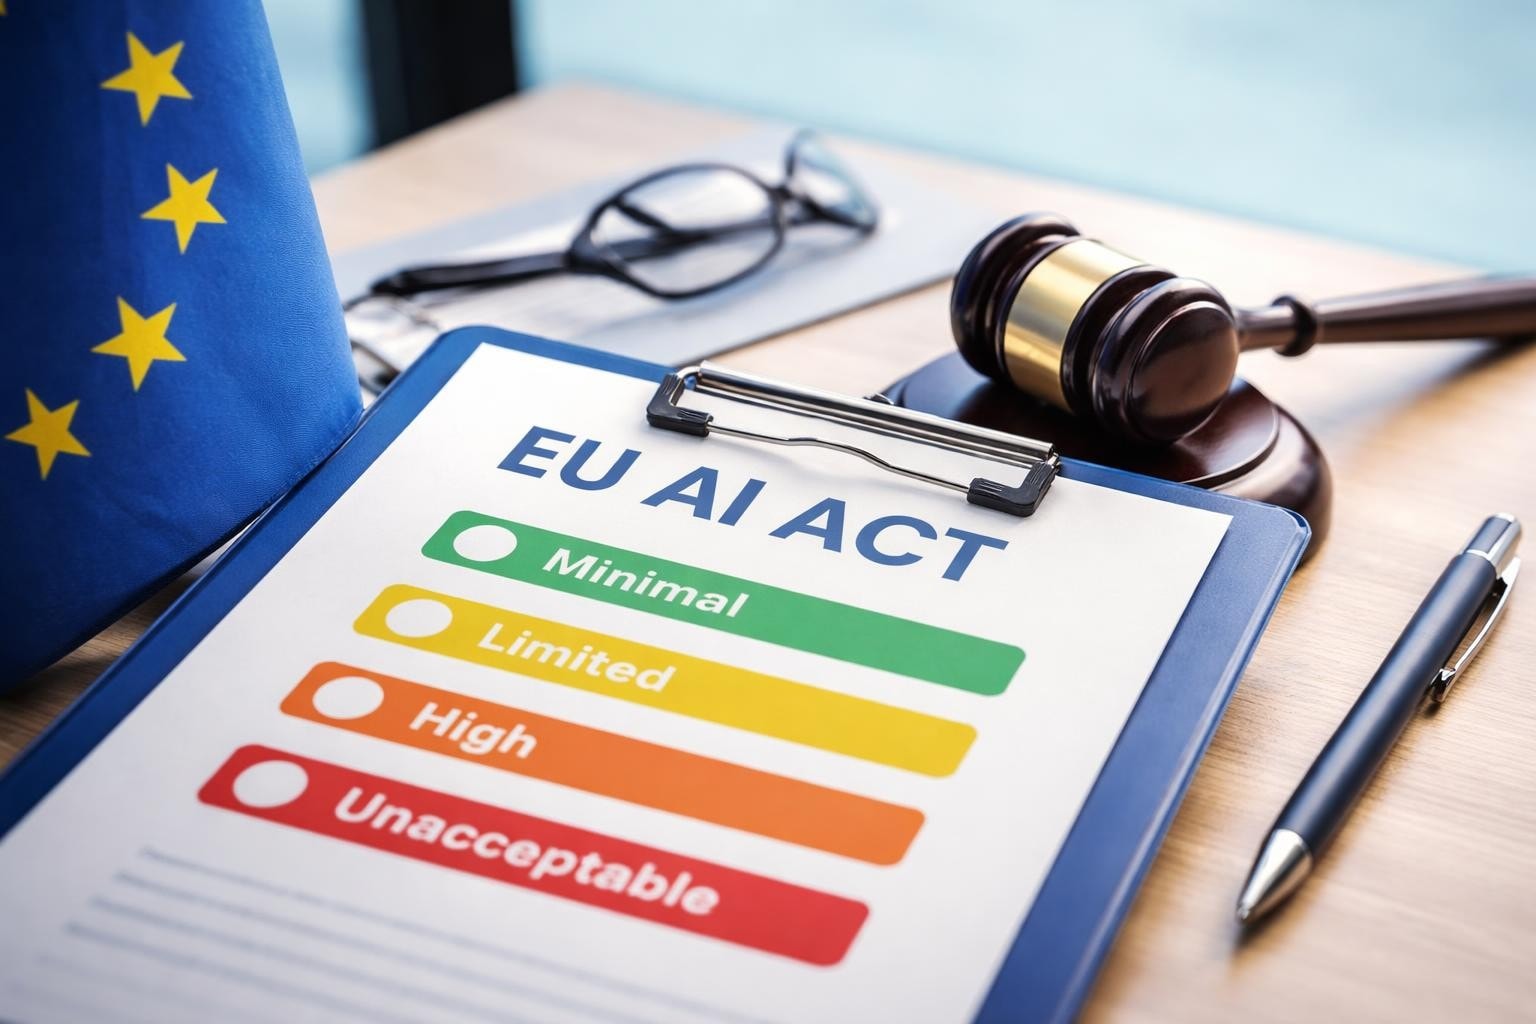
The regulatory framework for AI divides artificial intelligence systems into four distinct risk categories, each carrying different obligations and compliance requirements. This classification system forms the foundation of the eu act ai and determines what steps your organisation must take.
The Four Risk Categories Explained
Unacceptable risk systems are entirely prohibited under the eu act ai. These include AI applications that manipulate human behaviour through subliminal techniques, exploit vulnerabilities of specific groups, enable social scoring by governments, or conduct real-time biometric identification in public spaces by law enforcement (with limited exceptions).
High-risk AI systems face the strictest requirements. These applications must undergo conformity assessments, maintain detailed documentation, and implement robust risk management systems. The risk-based approach identifies high-risk systems across eight specific areas:
Biometric identification and categorisation
Critical infrastructure management
Educational and vocational training
Employment and worker management
Access to essential services
Law enforcement applications
Migration and border control
Administration of justice and democratic processes
Limited risk systems require transparency obligations. Users must be informed when they're interacting with AI, such as chatbots or deepfake content. This category covers most generative AI applications deployed in customer-facing environments.
Minimal risk systems face no specific obligations beyond existing legislation. These include AI-powered spam filters, inventory management systems, and similar low-impact applications.
Key Compliance Requirements Under the EU Act AI
Organisations deploying high-risk AI systems must satisfy multiple stringent requirements. The eu act ai mandates a comprehensive approach to risk management, data governance, and ongoing monitoring that extends throughout the AI system's lifecycle.
Documentation and Record-Keeping Obligations
High-risk AI providers must maintain extensive technical documentation. This includes detailed descriptions of the AI system's design, development process, intended purpose, and performance metrics. Records must demonstrate compliance with eu act ai requirements and remain accessible to supervisory authorities.
Automatic logging capabilities are mandatory. Systems must record events throughout their operation, enabling traceability and accountability. These logs become critical evidence during audits or investigations into system failures or adverse outcomes.
Compliance Area | Requirement | Frequency |
Risk Assessment | Document potential harms and mitigation strategies | Before deployment and after significant changes |
Data Governance | Verify training data quality, relevance, and bias | Ongoing throughout lifecycle |
Human Oversight | Implement mechanisms for human intervention | Continuous monitoring |
Accuracy Metrics | Test and validate system performance | Regular intervals defined by risk level |
Transparency | Provide clear information to deployers and users | At deployment and updates |
Training Requirements for Staff and Users
One critical aspect often overlooked is the human element of AI deployment. The eu act ai explicitly requires that individuals deploying or using high-risk AI systems possess adequate AI literacy. This isn't merely a suggestion but a legal obligation embedded within Article 4 of the regulation.
Staff members must understand how AI systems operate, recognise their limitations, and identify potential risks or biases. They need practical knowledge about interpreting AI outputs, maintaining human oversight, and escalating concerns when systems behave unexpectedly.
For organisations seeking to meet these requirements efficiently, the AI Literacy Course for EU AI Act Compliance provides structured training aligned specifically with Article 4 obligations. These programmes ensure your workforce develops the competencies required under the regulation whilst maintaining productivity through self-paced, interactive modules.
Implementation Timeline and Enforcement Deadlines
The AI Act entered into force on 1 August 2024, triggering a phased implementation schedule. Understanding these deadlines is crucial for compliance planning, as different provisions take effect at different times.
Critical Dates for 2026 and Beyond
February 2025 marked the first major milestone when prohibitions on unacceptable risk AI systems became enforceable. Organisations deploying such systems faced immediate legal consequences, including substantial fines.
August 2026 brings the next significant deadline when obligations for general-purpose AI models take full effect. Providers of foundation models and large language models must comply with transparency requirements, technical documentation standards, and copyright provisions.
August 2027 represents the comprehensive enforcement date when all high-risk AI system requirements become mandatory. Organisations must have conformity assessments completed, technical documentation prepared, and risk management systems operational.
The staggered approach allows organisations time to adapt, but it also creates complexity. Different systems face different deadlines, requiring careful tracking and project management.
Penalties for Non-Compliance
The eu act ai establishes severe financial penalties for violations. These fines operate on a tiered system based on the infringement's severity and the organisation's size.
Prohibited AI practices: Up to €35 million or 7% of global annual turnover, whichever is higher
Non-compliance with obligations: Up to €15 million or 3% of global annual turnover
Supplying incorrect information: Up to €7.5 million or 1% of global annual turnover
For small and medium-sized enterprises, caps apply to prevent disproportionate impact, but penalties remain substantial enough to threaten business viability.
Governance Structures and Oversight Bodies
The eu act ai establishes a complex governance architecture involving multiple authorities at European and national levels. Understanding this structure helps organisations navigate compliance effectively.
The European Artificial Intelligence Board
This newly created body coordinates AI regulation across member states. It develops guidance documents, facilitates information exchange between national authorities, and ensures consistent implementation of the eu act ai throughout the European Union.
The Board includes representatives from each member state's supervisory authority plus the European Data Protection Supervisor, who plays a crucial role in ensuring AI systems respect fundamental rights and data protection principles.
National Competent Authorities
Each EU member state designates authorities responsible for eu act ai enforcement within its territory. These bodies conduct market surveillance, investigate complaints, and impose penalties for violations.
Organisations operating across multiple countries must engage with various national authorities, each potentially interpreting requirements slightly differently. This fragmentation creates compliance challenges that demand careful coordination.
Preparing Your Organisation for EU Act AI Compliance
Successful compliance requires systematic preparation across multiple organisational functions. The eu act ai impacts not just technology teams but legal, human resources, procurement, and executive leadership.
Conducting an AI System Inventory
Begin by cataloguing all AI systems your organisation develops, deploys, or procures. Many companies underestimate their AI footprint, overlooking embedded systems within third-party software or legacy applications incorporating machine learning components.
For each system, determine its risk classification under the eu act ai framework. High-risk systems demand immediate attention, but don't ignore limited-risk applications requiring transparency measures.
Building Cross-Functional Compliance Teams
AI governance cannot reside solely within IT departments. Effective compliance requires collaboration between:
Legal teams interpreting regulatory requirements and contractual obligations
Data protection officers ensuring GDPR alignment and privacy safeguards
Technical specialists implementing security measures and testing protocols
Business leaders understanding operational impacts and resource allocation
Human resources developing training programmes and competency frameworks
Regular coordination meetings keep stakeholders aligned and identify emerging challenges before they escalate into compliance failures.
Establishing Vendor Management Protocols
Many organisations rely on third-party AI solutions rather than developing systems internally. The eu act ai creates shared responsibility between providers and deployers, making vendor selection and management critical.
Due diligence processes must verify that suppliers comply with applicable eu act ai requirements. Contracts should clearly allocate responsibilities, mandate documentation provision, and establish audit rights. Don't assume vendors handle compliance automatically, as recent analysis of AI regulation reveals significant gaps in many provider practices.
Practical Steps for Immediate Implementation
Theory matters little without practical action. Organisations must translate eu act ai requirements into concrete operational changes that embed compliance into daily workflows.
Developing Risk Management Frameworks
High-risk AI systems require comprehensive risk management throughout their lifecycle. This process begins during system design and continues through deployment, monitoring, and eventual retirement.
Identify potential harms the AI system might cause. Consider accuracy failures, security vulnerabilities, privacy breaches, discriminatory outcomes, and unintended consequences. Document mitigation strategies for each identified risk and implement monitoring mechanisms to detect emerging issues.
Risk management isn't a one-time exercise. Regular reviews ensure the framework adapts to changing circumstances, new use cases, and evolving threats.
Implementing Human Oversight Mechanisms
The transparency requirements of the eu act ai mandate meaningful human oversight of high-risk systems. This means more than simply having humans in the loop; it requires empowering individuals to understand, question, and override AI decisions when appropriate.
Design interfaces that present AI recommendations clearly, highlighting confidence levels and key factors influencing outputs. Provide mechanisms for humans to reject or modify AI-generated decisions without excessive friction that discourages intervention.
Train oversight personnel thoroughly. They must possess sufficient AI literacy to recognise when systems behave abnormally and understand the limitations inherent in algorithmic decision-making.
Establishing Testing and Validation Procedures
Before deploying high-risk AI systems, rigorous testing verifies they meet accuracy, security, and fairness standards. The eu act ai requires validation using appropriate datasets that represent the diversity of real-world deployment scenarios.
Testing protocols should assess:
Accuracy rates across different demographic groups and use cases
Robustness against adversarial inputs and edge cases
Security against unauthorised access and data poisoning
Bias metrics revealing discriminatory patterns in outputs
Performance degradation over time as data distributions shift
Document all testing results meticulously. These records demonstrate compliance during audits and provide baselines for ongoing monitoring.
Building AI Literacy Across Your Workforce
Compliance with the eu act ai ultimately depends on people, not just processes. Developing organisational AI literacy transforms regulatory requirements from bureaucratic burdens into opportunities for competitive advantage.
Identifying Training Needs by Role
Different roles require different levels of AI understanding. Executives need strategic awareness of regulatory landscapes and business implications. Developers require deep technical knowledge about bias mitigation and security practices. End users need practical skills for responsible AI interaction.
Conduct skills assessments identifying gaps between current capabilities and eu act ai requirements. Prioritise training investments based on compliance urgency and business impact.
Selecting Effective Training Approaches
Traditional classroom training often fails to deliver lasting AI literacy, particularly given the rapid evolution of both technology and regulation. Self-paced, interactive courses prove more effective, allowing learners to progress at comfortable speeds whilst maintaining engagement through practical exercises.
Multilingual accessibility matters for organisations operating across Europe. The eu act ai applies uniformly across member states, but training effectiveness improves dramatically when delivered in learners' native languages. Platforms offering AI literacy training in over 30 languages remove linguistic barriers that impede comprehension and retention.
Measuring Training Effectiveness
Compliance requires demonstrable competency, not merely attendance records. Assessment mechanisms verify that learners genuinely understand AI concepts and can apply knowledge in practical scenarios.
Track completion rates, assessment scores, and post-training behaviour changes. Monitor whether trained staff demonstrate improved decision-making around AI systems, more frequent identification of potential issues, and stronger adherence to governance protocols.
Integrating EU Act AI Compliance with Existing Frameworks
Most organisations already operate under multiple regulatory regimes. The eu act ai doesn't exist in isolation but intersects with data protection, consumer rights, employment law, and sector-specific regulations.
Aligning with GDPR Requirements
The General Data Protection Regulation and the eu act ai overlap significantly, particularly regarding automated decision-making, data quality, and individual rights. Organisations often find that strong GDPR compliance provides a foundation for eu act ai adherence.
Both regulations emphasise transparency, fairness, and accountability. Data minimisation principles under GDPR complement the eu act ai's focus on appropriate dataset curation. Privacy impact assessments required for high-risk processing often identify concerns relevant to AI risk management frameworks.
Sector-Specific Regulatory Integration
Financial services, healthcare, and other regulated industries face additional compliance layers beyond the general eu act ai requirements. Banking institutions must satisfy prudential regulation whilst deploying AI for credit decisions. Healthcare providers must maintain patient safety standards when implementing diagnostic AI tools.
Integrated compliance frameworks prevent duplication and inconsistency. Map eu act ai obligations against existing regulatory requirements, identifying overlaps and gaps. Unified governance structures address multiple regulations simultaneously, reducing administrative burden and improving coherence.
Future Developments and Ongoing Adaptation
The eu act ai represents living legislation that will evolve as AI technology advances and implementation experience accumulates. Organisations must maintain awareness of regulatory developments and adapt compliance programmes accordingly.
Anticipated Guidance and Standards
European standardisation bodies are developing harmonised standards that provide presumption of conformity with eu act ai requirements. Systems meeting these standards benefit from streamlined compliance verification.
The European Commission continues publishing guidance documents clarifying ambiguous provisions and addressing emerging questions. National authorities issue interpretative notes reflecting local enforcement priorities.
Staying current requires monitoring multiple information sources and participating in industry forums where regulatory developments are discussed. This ongoing engagement transforms compliance from reactive burden into proactive strategic advantage.
Emerging Technologies and Regulatory Scope
Generative AI, autonomous systems, and brain-computer interfaces push the boundaries of existing regulatory frameworks. The eu act ai's technology-neutral approach provides flexibility, but novel applications create uncertainty about classification and applicable requirements.
Organisations pioneering innovative AI applications should engage with regulators early, seeking clarity about compliance pathways before making substantial development investments. This proactive dialogue helps shape practical implementation of the eu act ai whilst demonstrating good-faith compliance efforts.
The eu act ai fundamentally reshapes how organisations develop, deploy, and govern artificial intelligence systems across Europe. Compliance demands systematic preparation spanning technology, processes, and people, with particular emphasis on building genuine AI literacy throughout the workforce. GURO (myaitraining.eu) provides the essential training foundation organisations need to meet Article 4 requirements efficiently. Our AI literacy courses deliver practical, interactive learning aligned precisely with eu act ai obligations, available in over 30 languages to support your entire European workforce. Start building compliance-ready AI capabilities today through structured training that transforms regulatory requirements into competitive advantages.
Comments