
The AI Act EU: Comprehensive Guide for Businesses in 2026
The European Union has fundamentally reshaped the global artificial intelligence landscape through its landmark legislation. As organisations across Europe and beyond navigate this new regulatory environment, understanding the ai act eu has become essential for business continuity and competitive advantage. This comprehensive framework represents the world's first major attempt to regulate artificial intelligence systems based on risk, establishing clear obligations for developers and deployers whilst protecting fundamental rights and safety. For businesses operating in or with the European market, compliance is no longer optional but a strategic imperative that demands immediate attention and systematic preparation.
Understanding the Risk-Based Framework of the AI Act EU
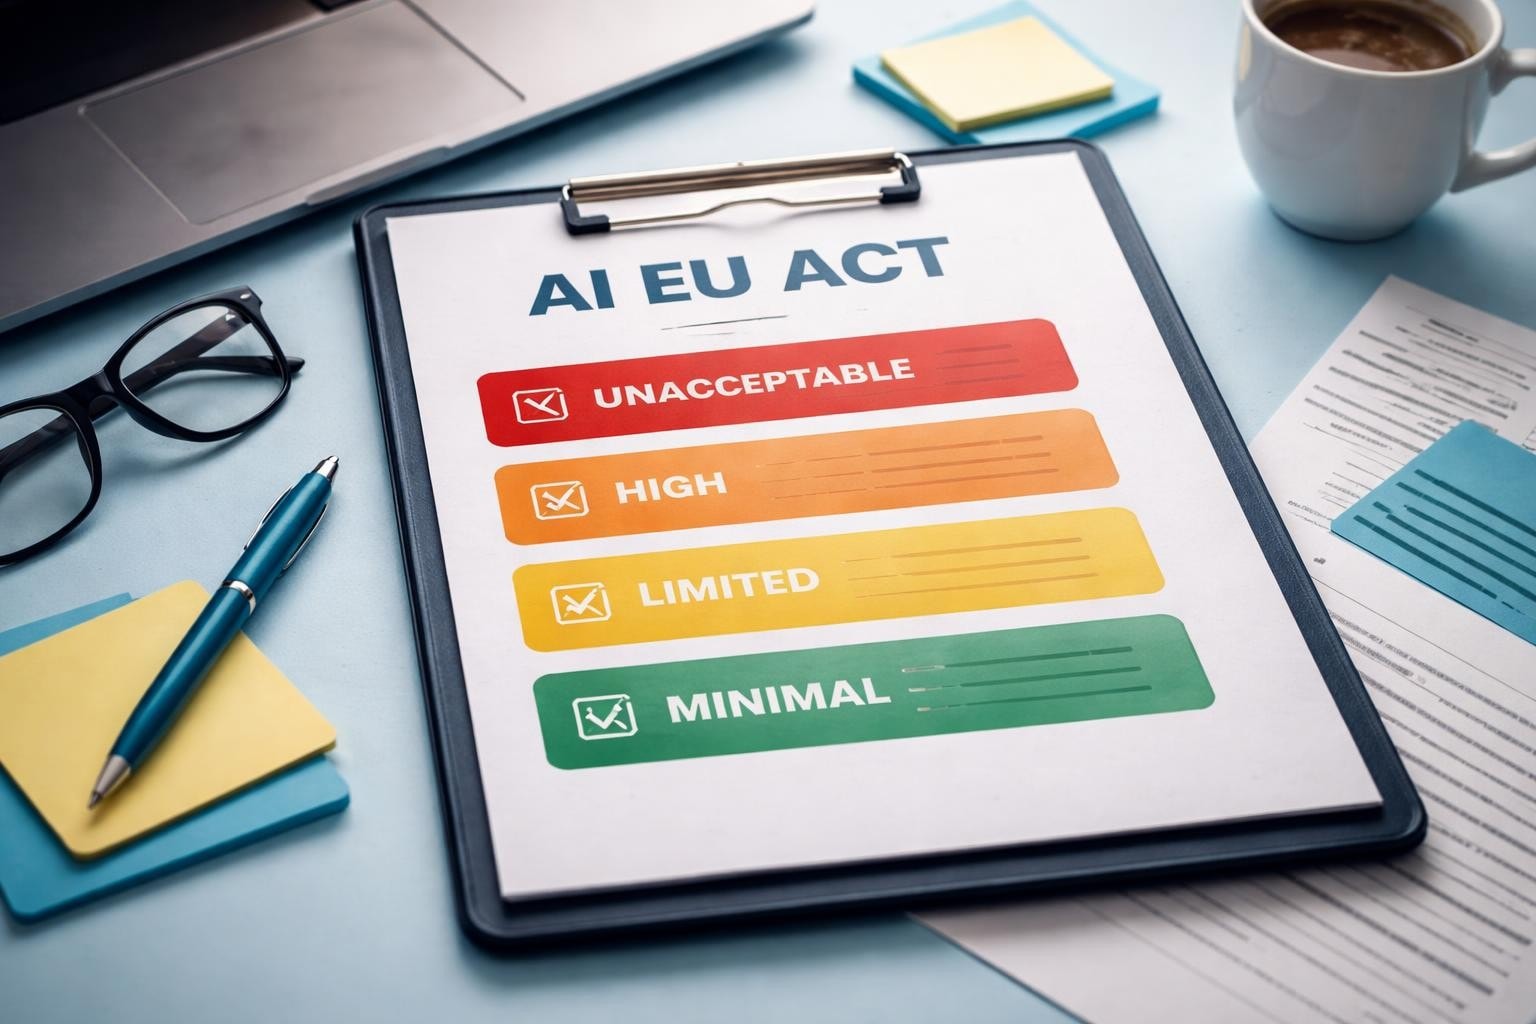
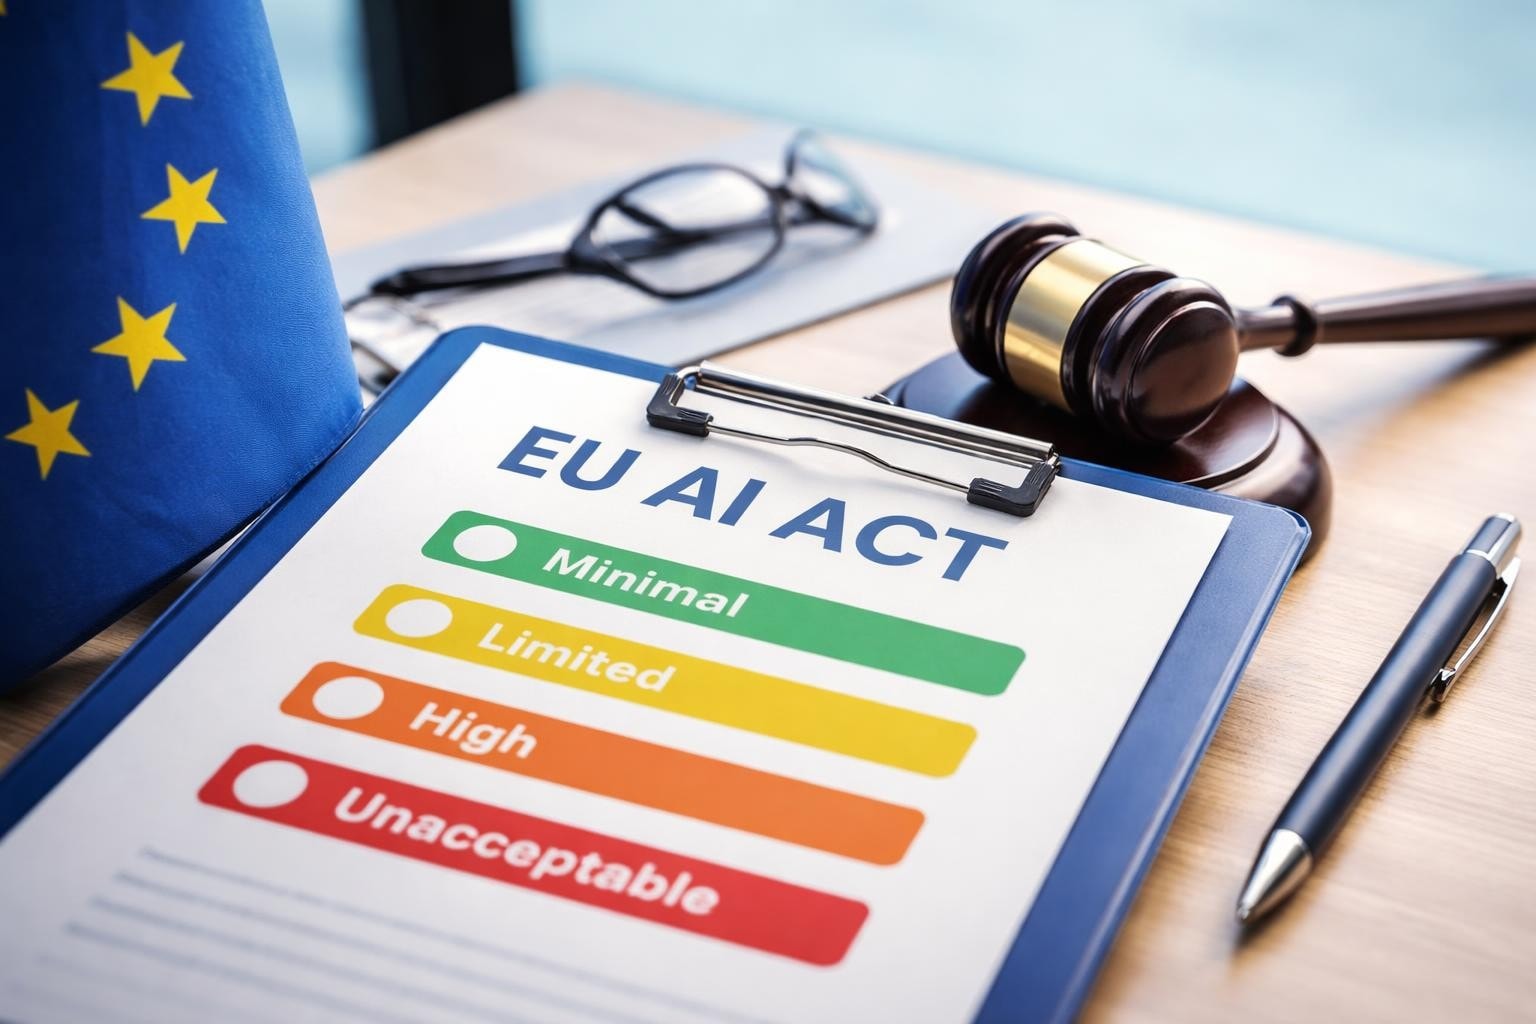
The ai act eu establishes a sophisticated classification system that categorises artificial intelligence applications according to their potential impact on individuals and society. This risk-based approach creates four distinct tiers, each carrying different regulatory burdens and compliance requirements.
Unacceptable Risk Systems
The regulation completely prohibits certain AI applications deemed to pose unacceptable risks to fundamental rights. These banned systems include:
Social scoring mechanisms that evaluate or classify individuals based on behaviour, socio-economic status, or personal characteristics
Real-time biometric identification in publicly accessible spaces for law enforcement purposes (with limited exceptions)
Subliminal manipulation techniques that exploit vulnerabilities of specific groups
Exploitative AI systems that take advantage of children or persons with disabilities
Organisations deploying such systems face immediate cessation orders and substantial penalties, making it critical to audit existing AI deployments against these prohibited categories.
High-Risk AI Applications
High-risk systems receive the most stringent regulatory scrutiny under the ai act eu framework. These applications span critical infrastructure, education, employment, essential services, law enforcement, migration management, and administration of justice.
Sector | Examples | Key Obligations |
Employment | CV screening, promotion decisions | Human oversight, bias testing, documentation |
Critical Infrastructure | Water, gas, electricity management | Risk management systems, quality data |
Education | Exam scoring, admission decisions | Transparency, accuracy requirements |
Law Enforcement | Predictive policing, evidence assessment | Fundamental rights impact assessments |
High-risk AI providers must establish comprehensive risk management systems, maintain detailed technical documentation, ensure data quality and governance, enable meaningful human oversight, and achieve appropriate levels of accuracy, robustness, and cybersecurity. Understanding these requirements helps organisations allocate resources effectively for compliance programmes.
Limited and Minimal Risk Categories
Limited risk AI systems, such as chatbots or deepfake generators, require transparency obligations ensuring users understand they're interacting with artificial intelligence. Minimal risk systems face no specific obligations beyond voluntary codes of practice, though organisations may choose to adopt best practices for competitive differentiation and stakeholder trust.
Compliance Requirements and Implementation Timelines
The phased implementation of the ai act eu provides organisations with structured timelines for achieving compliance, though certain provisions demand immediate attention in 2026.
Immediate Priority Areas:
Prohibited AI systems must be discontinued within six months of the regulation taking effect
General-purpose AI models require compliance frameworks aligned with transparency requirements
High-risk system developers must begin conformity assessment preparations
All organisations should commence AI system inventories and risk classifications
The staggered approach allows businesses to prioritise resources strategically. By mid-2026, organisations deploying high-risk AI systems must demonstrate compliance with the full regulatory framework, including technical documentation, quality management systems, and conformity assessment procedures.
For enterprises managing multiple AI deployments, establishing a centralised compliance function proves essential. This team coordinates risk assessments, maintains documentation repositories, liaises with regulatory authorities, and ensures ongoing monitoring of AI system performance against regulatory standards.
Documentation and Transparency Standards
The ai act eu mandates extensive documentation throughout the AI system lifecycle. High-risk system providers must maintain technical files containing:
Detailed descriptions of system design and development processes
Training, validation, and testing data specifications
Risk management methodology and implementation evidence
Human oversight measures and their effectiveness
Performance metrics demonstrating accuracy and robustness
Cybersecurity measures protecting system integrity
This documentation must remain accessible to competent authorities for ten years following system deployment. The enterprise data implications extend beyond simple record-keeping, requiring robust data governance infrastructures capable of demonstrating compliance at scale.
General-Purpose AI Models and Foundation Systems
The ai act eu introduces specific provisions for general-purpose AI (GPAI) models, recognising their unique characteristics and widespread deployment potential. These large-scale models, including foundation models and generative AI systems, face tiered obligations based on their capabilities and systemic impact.
Baseline Requirements for GPAI Providers
All general-purpose AI model providers must ensure technical documentation accompanies their systems, comply with copyright law requirements for training data, and publish detailed summaries of training content. The voluntary code of practice released by the European Union provides practical guidance for meeting these transparency obligations whilst maintaining competitive positioning.
Systemic Risk Models
GPAI models with systemic risk characteristics trigger additional obligations. The regulation identifies such models based on computational power thresholds or demonstrated high-impact capabilities. Providers must:
Conduct model evaluations identifying and mitigating systemic risks
Perform adversarial testing to identify vulnerabilities
Track and report serious incidents to regulatory authorities
Ensure adequate cybersecurity protections throughout the model lifecycle
These enhanced requirements reflect the potential for powerful AI systems to generate cascading effects across multiple applications and sectors, demanding proactive risk management at the foundational level.
Enforcement Mechanisms and Penalty Structure
The ai act eu establishes a robust enforcement framework with significant financial penalties designed to ensure meaningful compliance across organisations of all sizes. Understanding these consequences helps businesses justify compliance investments and prioritise risk mitigation strategies.
Violation Type | Maximum Fine | Calculation Basis |
Prohibited AI systems | €35 million or 7% global turnover | Whichever is higher |
Non-compliance with obligations | €15 million or 3% global turnover | Whichever is higher |
Inaccurate information to authorities | €7.5 million or 1% global turnover | Whichever is higher |
Beyond financial penalties, enforcement actions may include product recalls, deployment suspensions, and reputational damage that extends far beyond immediate monetary costs. For organisations operating across multiple jurisdictions, the ai act eu's extraterritorial reach means compliance obligations extend to non-EU entities whose AI systems affect European users or markets.
Building AI Literacy for Organisational Compliance
Successful navigation of the ai act eu framework requires more than legal expertise. It demands organisation-wide AI literacy ensuring employees at all levels understand artificial intelligence fundamentals, recognise regulatory obligations in their specific roles, and contribute effectively to compliance processes.
The Article 4 Mandate
Article 4 of the ai act eu specifically addresses AI literacy, requiring providers and deployers to ensure staff possess sufficient understanding of AI systems, their capabilities, and their limitations. This provision recognises that technical compliance measures alone cannot guarantee responsible AI deployment without human understanding and oversight.
Organisations meeting Article 4 requirements demonstrate measurable competency across their workforce in areas including:
Basic AI concepts and terminology relevant to business contexts
Understanding of the risk-based classification system
Recognition of bias, fairness, and transparency considerations
Practical application of human oversight principles
Documentation and reporting requirements for deployed systems
For businesses seeking efficient compliance with Article 4, structured training programmes aligned with regulatory requirements provide the foundation for sustainable AI governance. The AI Literacy Course for EU AI Act Compliance offers scalable solutions designed specifically for organisations navigating these obligations, with flexible pricing tiers accommodating teams from 20 employees to enterprise-scale deployments.
Integrating AI Literacy Across Functions
Effective AI literacy programmes extend beyond technical teams to encompass procurement specialists evaluating vendor AI systems, human resources professionals deploying recruitment tools, marketing teams leveraging generative AI, customer service managers implementing chatbots, and executive leadership making strategic AI investment decisions.
This cross-functional approach ensures compliance responsibilities distribute appropriately throughout organisational structures rather than concentrating exclusively within legal or IT departments. When procurement understands high-risk AI criteria, they can conduct more effective due diligence on vendor solutions. When marketing teams recognise transparency obligations, they implement disclosure mechanisms proactively rather than reactively.
Sector-Specific Implications and Applications
The ai act eu's impact varies significantly across industries, with certain sectors facing particularly complex compliance landscapes due to the nature of their AI deployments.
Healthcare and Medical Devices
Medical AI systems generally qualify as high-risk under the regulation, triggering comprehensive compliance obligations. Digital medical products must navigate both the AI Act and existing medical device regulations, creating overlapping compliance requirements that demand careful coordination.
Diagnostic AI tools, treatment recommendation systems, patient monitoring applications, and medical imaging analysis platforms all require robust validation demonstrating clinical safety and effectiveness alongside AI-specific requirements for transparency and human oversight.
Financial Services
Banking, insurance, and investment sectors deploy AI extensively for credit scoring, fraud detection, risk assessment, and automated trading. Many of these applications fall within high-risk categories, particularly those affecting access to essential services or making decisions about individuals' financial standing.
Financial institutions must balance AI innovation with stringent regulatory compliance, ensuring algorithmic decision-making systems maintain auditability, explainability, and fairness whilst meeting existing financial services regulations.
Public Sector and Administration
Government agencies face unique challenges implementing the ai act eu framework. Public sector AI deployments in areas like social benefits administration, immigration processing, and public service allocation often qualify as high-risk, requiring particularly rigorous safeguards given their impact on fundamental rights and access to essential services.
Public procurement processes must incorporate AI Act compliance criteria when selecting systems, and government agencies must ensure adequate technical capacity for ongoing monitoring and oversight of deployed AI solutions.
International Implications and the Brussels Effect
Whilst the ai act eu applies formally within European Union member states, its influence extends globally through market dynamics and regulatory emulation. The potential Brussels Effect describes how EU regulations often become de facto global standards as multinational organisations adopt unified compliance approaches rather than maintaining separate systems for different markets.
Global Business Strategies
Companies serving European markets whilst operating primarily outside the EU face strategic decisions about compliance scope. Many organisations choose comprehensive adoption of AI Act standards across their entire operations, recognising benefits including:
Simplified compliance management without jurisdiction-specific variations
Enhanced stakeholder trust through alignment with rigorous regulatory standards
Competitive positioning in markets increasingly valuing responsible AI
Preparation for potential regulatory convergence as other jurisdictions adopt similar frameworks
This globalisation of EU AI standards mirrors previous patterns with data protection regulations, where GDPR principles influenced privacy practices worldwide despite its European origin.
Emerging International Alignment
Other jurisdictions are developing AI regulatory frameworks with varying degrees of alignment to the ai act eu approach. Understanding these parallel developments helps organisations anticipate future compliance landscapes and identify opportunities for leveraging existing AI Act preparations across multiple regulatory regimes.
Some nations adopt risk-based frameworks similar to the EU model, whilst others pursue sector-specific approaches or rely primarily on industry self-regulation. Monitoring these divergent paths enables businesses to develop flexible compliance architectures accommodating multiple regulatory models without duplicating foundational governance investments.
Practical Steps for Immediate Compliance Preparation
Organisations beginning their ai act eu compliance journey should prioritise several foundational activities that create value regardless of specific system classifications or deployment timelines.
Conduct Comprehensive AI System Inventory:
Start by identifying all AI systems currently deployed or under development across the organisation. This inventory should capture system purposes, data sources, decision-making roles, affected populations, and responsible business units. Many organisations discover previously unknown AI deployments during this process, particularly consumer-grade AI tools adopted informally by individual teams.
Establish Risk Classification Methodology:
Develop systematic processes for evaluating AI systems against the ai act eu risk categories. This methodology should incorporate both initial classifications for new systems and periodic reassessments for existing deployments as systems evolve or regulatory interpretations develop.
Create Governance Structures:
Designate clear accountability for AI compliance at board, executive, and operational levels. Effective governance frameworks include executive sponsors for AI strategy, cross-functional compliance committees, system-level responsible officers, and escalation pathways for risk identification and mitigation.
Invest in Documentation Infrastructure:
Implement systems capable of capturing and maintaining the extensive documentation required throughout AI lifecycles. Consider purpose-built AI governance platforms or configure existing enterprise systems to accommodate AI-specific documentation requirements whilst ensuring accessibility for regulatory inspections.
Develop Vendor Management Protocols:
For organisations deploying third-party AI systems, establish processes ensuring vendors provide necessary compliance documentation, contractual provisions allocating AI Act responsibilities, ongoing monitoring of vendor compliance status, and contingency plans addressing potential vendor non-compliance.
The Role of Continuous Monitoring and Adaptation
The ai act eu compliance represents an ongoing commitment rather than a one-time achievement. AI systems evolve through retraining, updates, and deployment in new contexts, potentially altering their risk classifications or compliance requirements.
Establishing continuous monitoring processes ensures organisations identify when system changes trigger new obligations, performance metrics indicate potential compliance issues, regulatory guidance evolves or clarifies existing requirements, and incident patterns suggest systematic compliance gaps requiring remediation.
This dynamic compliance approach aligns with the regulation's focus on lifecycle management, recognising that responsible AI deployment demands sustained attention throughout system operation rather than solely at development and deployment stages.
Effective monitoring programmes combine automated technical controls tracking system performance and behaviour, regular human review evaluating compliance against current regulatory interpretations, stakeholder feedback mechanisms identifying real-world impact concerns, and periodic third-party assessments providing independent validation of compliance claims.
The ai act eu establishes a comprehensive regulatory framework that demands strategic preparation and sustained commitment from organisations deploying artificial intelligence systems. By understanding risk classifications, implementing robust governance structures, and building organisation-wide AI literacy, businesses can navigate compliance requirements whilst leveraging AI's transformative potential responsibly. GURO provides AI Literacy courses fully aligned with Article 4 requirements, offering practical, self-paced learning in over 30 languages to help your organisation build the foundational understanding essential for AI Act compliance. Explore how structured AI literacy training can transform your compliance journey into a competitive advantage.
Comments